


 README

Miabi
The open-source, self-hosted PaaS for shipping apps, not infrastructure.
Docker Compose isn't enough. Kubernetes is overkill. Miabi is the middle.
Quick Start · Live Demo · Features · Comparison · Architecture · Docs



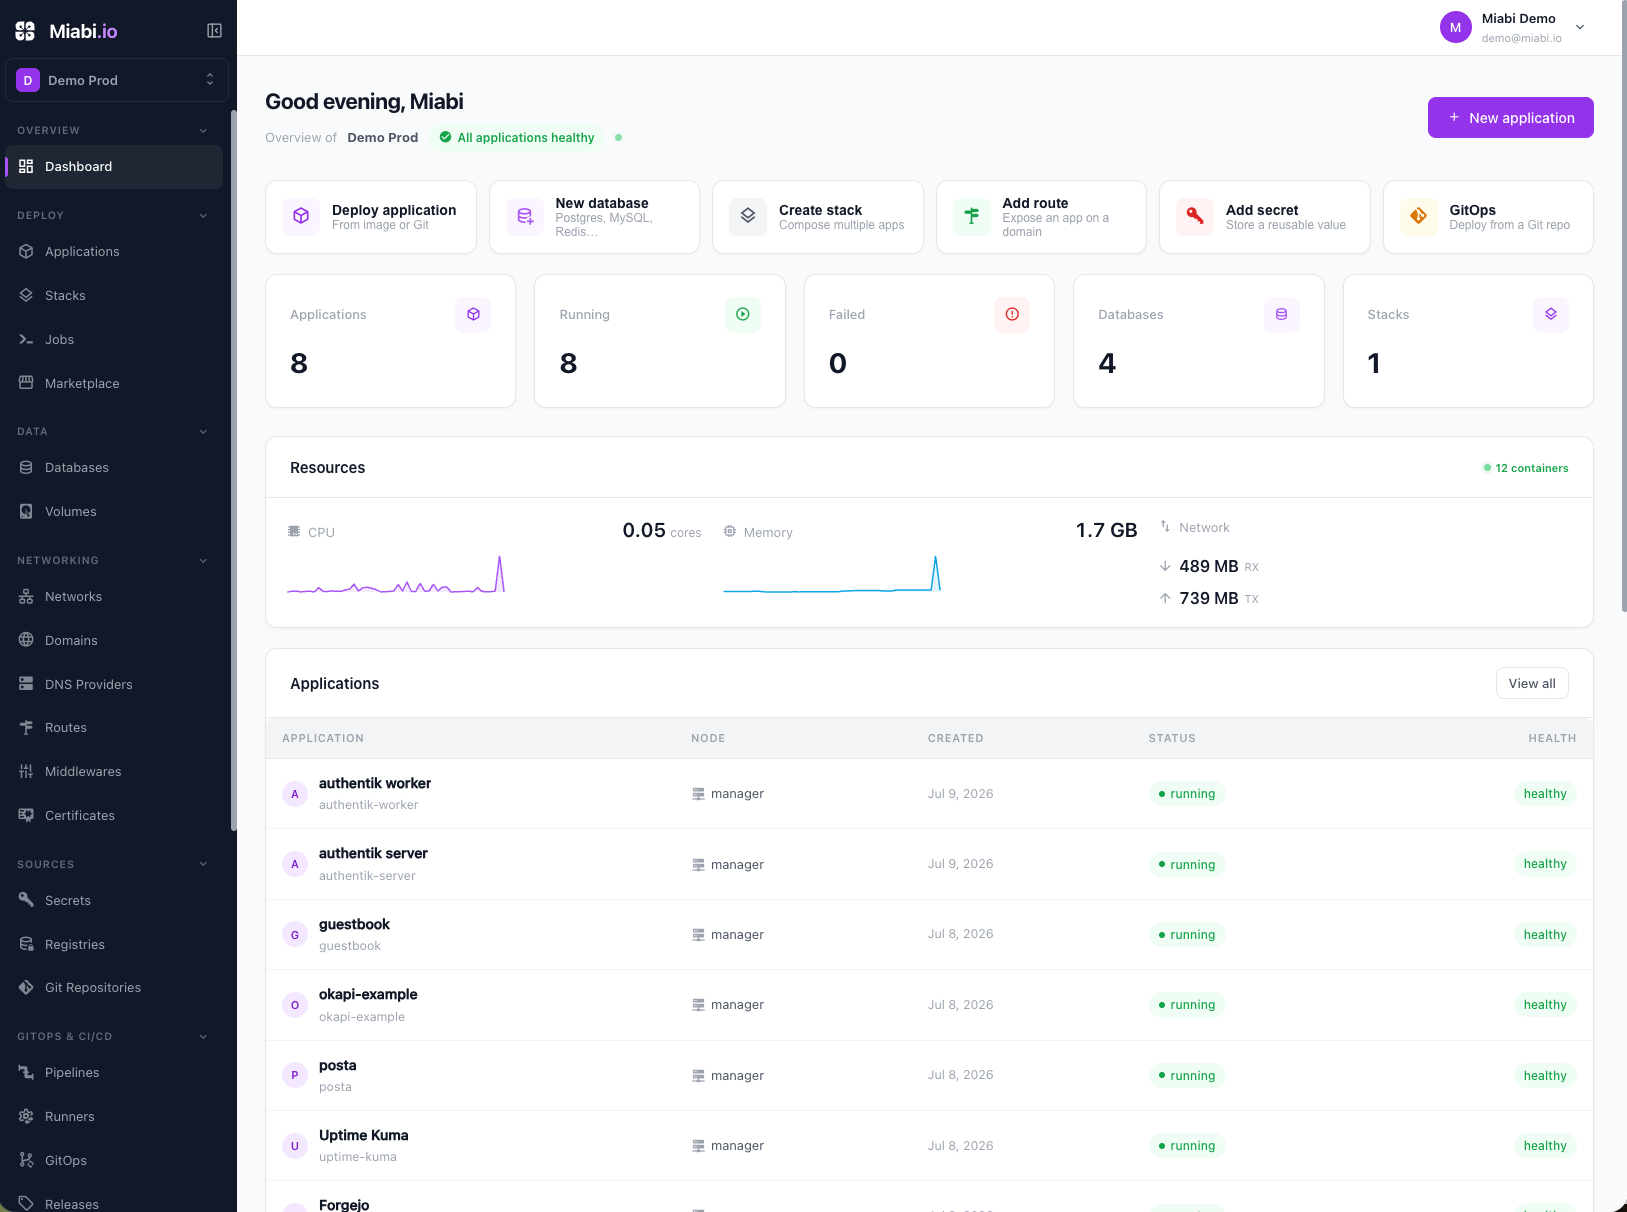
Miabi is a self-hosted, developer-first Platform-as-a-Service for containerized apps. Push an app — from a Git repo, a Docker image, or a marketplace template — and Miabi handles build, deploy, domains, TLS, databases, scaling, backups, monitoring, and analytics. One web console, one binary, no Docker commands and no Kubernetes cluster.
It is a fully self-hostable alternative to Heroku, Render, and Railway: your VPS, dedicated box, homelab, or cloud VM, with complete ownership of the infrastructure, the data, and the runtime.
The name. Miabi is Tshiluba (Kasai, DR Congo 🇨🇩) for the muabi trees, traditionally associated with blessing and growth. It joins the same family as its siblings Goma Gateway and Posta.
Contents
- Quick Start
- Why Miabi
- Features
- Screenshots
- How Miabi compares
- Architecture
- Live Demo
- Development
- Ecosystem
- Support & contributing
- License
Quick Start
Requirements: a Linux host with a reachable Docker socket, a domain pointing at it, and ports 80/443 free. PostgreSQL and Redis are brought up as part of the stack.
curl -fsSL https://get.miabi.io | sudo MIABI_DOMAIN=miabi.example.com \
  MIABI_ADMIN_EMAIL=you@example.com bash
The script installs Docker if missing, installs the miabi CLI, brings up the stack, and prints the admin password. From there:
sudo miabi stack status
sudo miabi stack restart
sudo miabi upgrade
sudo miabi stack uninstall
Other install paths — CLI, no root, Docker Compose
Install the CLI and run the same converge yourself:
sudo miabi setup --domain miabi.example.com --admin-email you@example.com
Or use no binary at all. The Miabi image is an installer too, which is the path to take when you don't have root:
docker run --rm -it \
  -v /var/run/docker.sock:/var/run/docker.sock \
  -v /etc/miabi:/etc/miabi \
  miabi/miabi:latest install --domain miabi.example.com --admin-email you@example.com
install, upgrade, restart, status, and uninstall on the image are the same commands as miabi setup / miabi upgrade / miabi stack … — one implementation, two front-ends, so neither can drift from the other. Either way the converge is idempotent: re-run it and only what changed is recreated.
Prefer to drive Compose yourself? examples/compose/ brings up the same stack.
Full options, the /etc/miabi/miabi.yaml manifest, the built-in registry, and custom gateway config are in the installation docs.
Why Miabi
Docker Compose isn't enough for production: no rolling updates, no rollback, no TLS, no multi-tenancy. Kubernetes is overkill: a service mesh just for canary, Argo CD or Flux just for GitOps, and a platform team to keep it running.
Miabi sits in the middle — production deployment strategies on plain Docker, with the pieces you actually need built in rather than assembled.
Three things set it apart from other self-hosted PaaS options:
Multi-tenancy from day one. Most self-hosted PaaS tools assume one operator and one set of apps. Miabi is built around workspaces: every app, database, domain, volume, registry image, secret, backup, and deployment belongs to one. That makes it workable for shared hosting providers, agencies running client apps, SaaS platforms, internal developer platforms, and universities — not just single-tenant homelabs.
Deployment strategies without a mesh. Rolling and canary deployments with weighted traffic splitting, rollbacks, and zero-downtime updates, on Docker, because routing already flows through Goma Gateway.
Analytics with zero instrumentation. Every request already passes through the gateway, so every app gets HTTP traffic, latency, and privacy-first web analytics with no JS snippet, no SDK, and no code change.
Everything in the console is also in the REST API, the CLI, and the Terraform provider. Run it on a VPS, dedicated server, bare metal, homelab, or cloud. No vendor lock-in, no managed control plane.
Features
Applications & deployments
- Deploy from a Git repo (build), a Docker image (pull), or a marketplace template
- Buildpack builds with no Dockerfile required, with configurable memory and time limits
- Releases with one-click rollback and full deployment history
- Zero-downtime updates, canary aliases, and weighted traffic splitting
- Env vars, a workspace secret vault, and per-app resource limits
- Jobs — one-off commands in an app's runtime context
- Stacks (compose-style app groups) and Environments (dev → staging → prod)
- Per-app timeline of lifecycle events
- Built-in container registry, multi-tenant and namespaced per workspace, with local or S3/MinIO storage and an optional garbage collector:
docker login <registry> -u <workspace-name> -p <api-token>
Domains, networking & TLS
- Domains with DNS-verified ownership, routed through Goma Gateway with workspace-owned middlewares
- Automatic TLS — HTTP-01 ACME by default, managed wildcard / DNS-01 certs via a connected DNS provider (auto-renewed), and uploaded custom certs (encrypted)
- Workspace-isolated Docker networks carved from a managed address pool, so a busy multi-tenant host never exhausts Docker's small default pool
- Configurable CIDR for the shared proxy network, per-node edge gateways, and on-demand port forwarding to managed databases
Data, storage & backups
- Databases — PostgreSQL, MySQL, MariaDB, Redis, libSQL, and MongoDB, with managed credentials and in-place version upgrades
- Volumes — workspace-owned Docker volumes, node-local by default, or shared (RWX) storage a replicated app can mount across nodes: NFS, CIFS/SMB, or a host-path bind to operator-managed storage under
/mnt/*(privileged workspaces) - Backups — scheduled and manual database backup/restore plus volume archives, to local, MinIO, or S3
Multi-node & clustering
- Nodes — add remote Docker hosts; the node agent dials the control plane over an outbound WebSocket tunnel, so it works behind NAT and firewalls
- Cluster mode — optional, auto-detected Docker Swarm with encrypted overlay networks
- Replicated service apps — in cluster mode apps deploy as replicated Swarm services by default (opt out per app); stateful apps with node-local storage stay pinned automatically
- Multiple clusters & locations — one control plane drives many clusters: the default cluster, standalone nodes connected over their agent tunnel, and remote Docker Swarms in other regions. Workspaces pick a location, and apps, databases and volumes are placed inside it
- Cluster ingress — each cluster is served by its own gateway (the central gateway, a node's own edge gateway, or a remote swarm's ingress node) with DNS pointing at it; traffic reaches a clustered app's tasks wherever the scheduler placed them, and the app detail view shows the real nodes replicas run on
- Node pools — group nodes by tier; Enterprise plan placement keeps each plan's workspaces on its locations and pool
- Image distribution — built images are pushed to the internal registry so any node can pull them, making multi-node deploys and rollbacks of Git-built apps work across the cluster
- Housekeeping to reconcile drift and reclaim disk, and Docker import to adopt pre-existing containers, volumes, and networks
CI/CD & GitOps
- Pipelines — pipeline-as-code CI/CD
- Build runners — dedicated build machines that keep build load off app-hosting nodes; a co-located runner ships for single-node and homelab use, and an optional "builds require a runner" guarantee keeps builds off production nodes entirely
- GitOps — declarative, pull-based reconciliation from
miabi.io/v1manifests, plus an imperative one-shot apply with dry-run, diff, and prune. No separate controller to run: no Argo CD, no Flux - Git push deploy, stored Git and registry credentials, signed webhooks, and notifications
- REST + OpenAPI everywhere, plus a CLI and an official Terraform / OpenTofu provider
Identity, teams & access
- Auth — registration, login with email or username, password reset, JWT sessions with Redis-backed revocation, API tokens, and 2FA (TOTP)
- SSO & directory — OAuth 2.0 / OIDC (GitHub, Google, generic OIDC). Enterprise adds SAML 2.0, SCIM provisioning, and LDAP / Active Directory sign-in on the normal login form, with directory groups mapped onto platform-admin and per-workspace roles
- Workspaces & teams — members, invitations, and organizations; each workspace has a unique name handle (its URL and
docker loginnamespace) plus a display name, and each user a unique username - RBAC — Owner · Admin · Developer · Viewer, enforced in middleware and by
workspace_idscoping. Enterprise adds custom roles and per-resource policies (a role on a single app, domain, or database) - Container security profiles — an optional non-root "restricted" profile runs app and job containers as a platform UID with
no-new-privileges; outbound webhooks are SSRF-guarded - Plans & quotas, per-workspace encryption keys (keyring/DEK), key rotation, and crypto-shred on delete
Monitoring, analytics & operations
- Container CPU/memory/disk metrics and workspace health with retained history, Prometheus integration, and health endpoints
- Analytics — requests/sec, status mix, bandwidth, top routes; p50/p95/p99 latency with a gateway-vs-upstream split ("is my app slow, or the gateway?"), error rate, and Apdex; unique visitors, top pages, referrers, countries, and device families. Cookieless, no consent banner, IPs never stored, unique visitors via HyperLogLog sketches rather than per-person rows
- Log storage — deployment, pipeline, job, and backup logs externalized from Postgres to a shared filesystem store with a bounded DB tail, retention, size caps, and full-log download; live tailing unchanged
- Append-only audit log of every mutating action, with optional SIEM streaming over syslog or webhook (Enterprise)
- Admin platform — nodes and cluster, users, plans, settings, OAuth providers, SSO, license, and SIEM
Marketplace
Official, versioned templates: WordPress, Ghost, Nextcloud, n8n, Gitea, Forgejo, Umami, NGINX, pgAdmin, phpMyAdmin, mongo-express, libSQL, Posta, PostgreSQL, MySQL, Redis, and MongoDB.
Screenshots
Deploy an application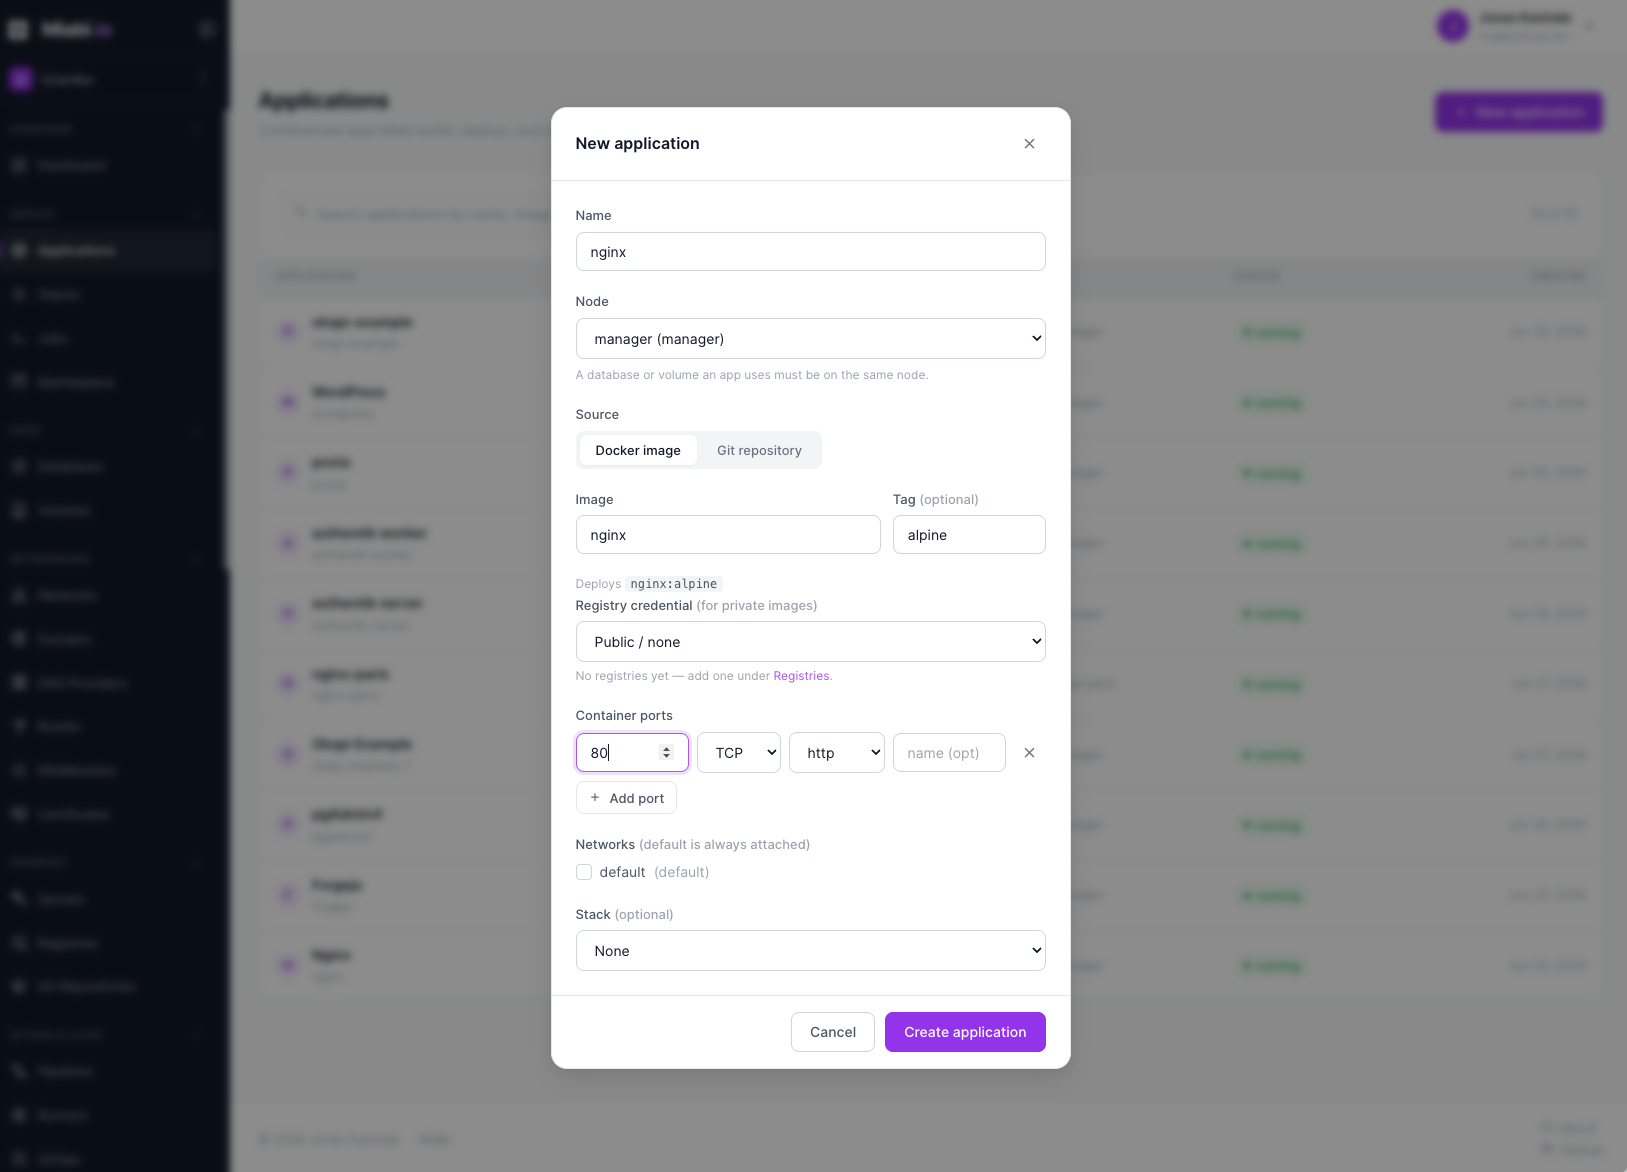 |
Canary deployment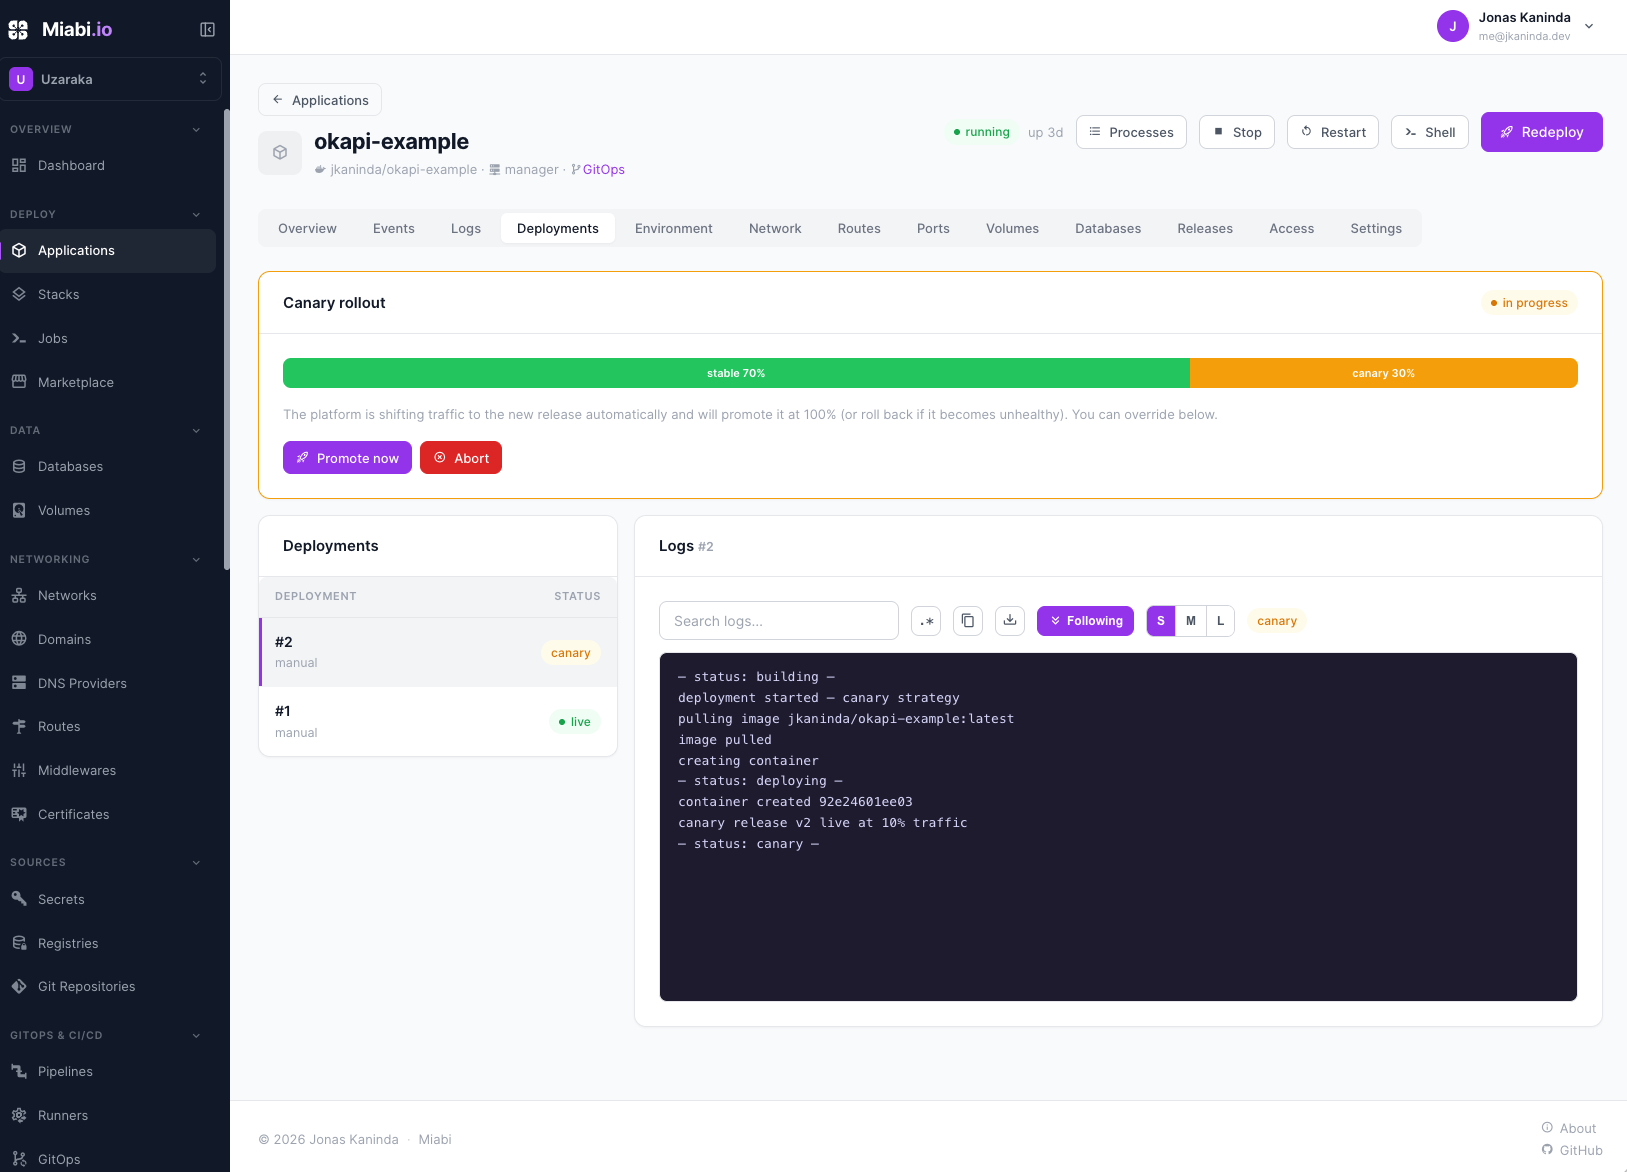 |
GitOps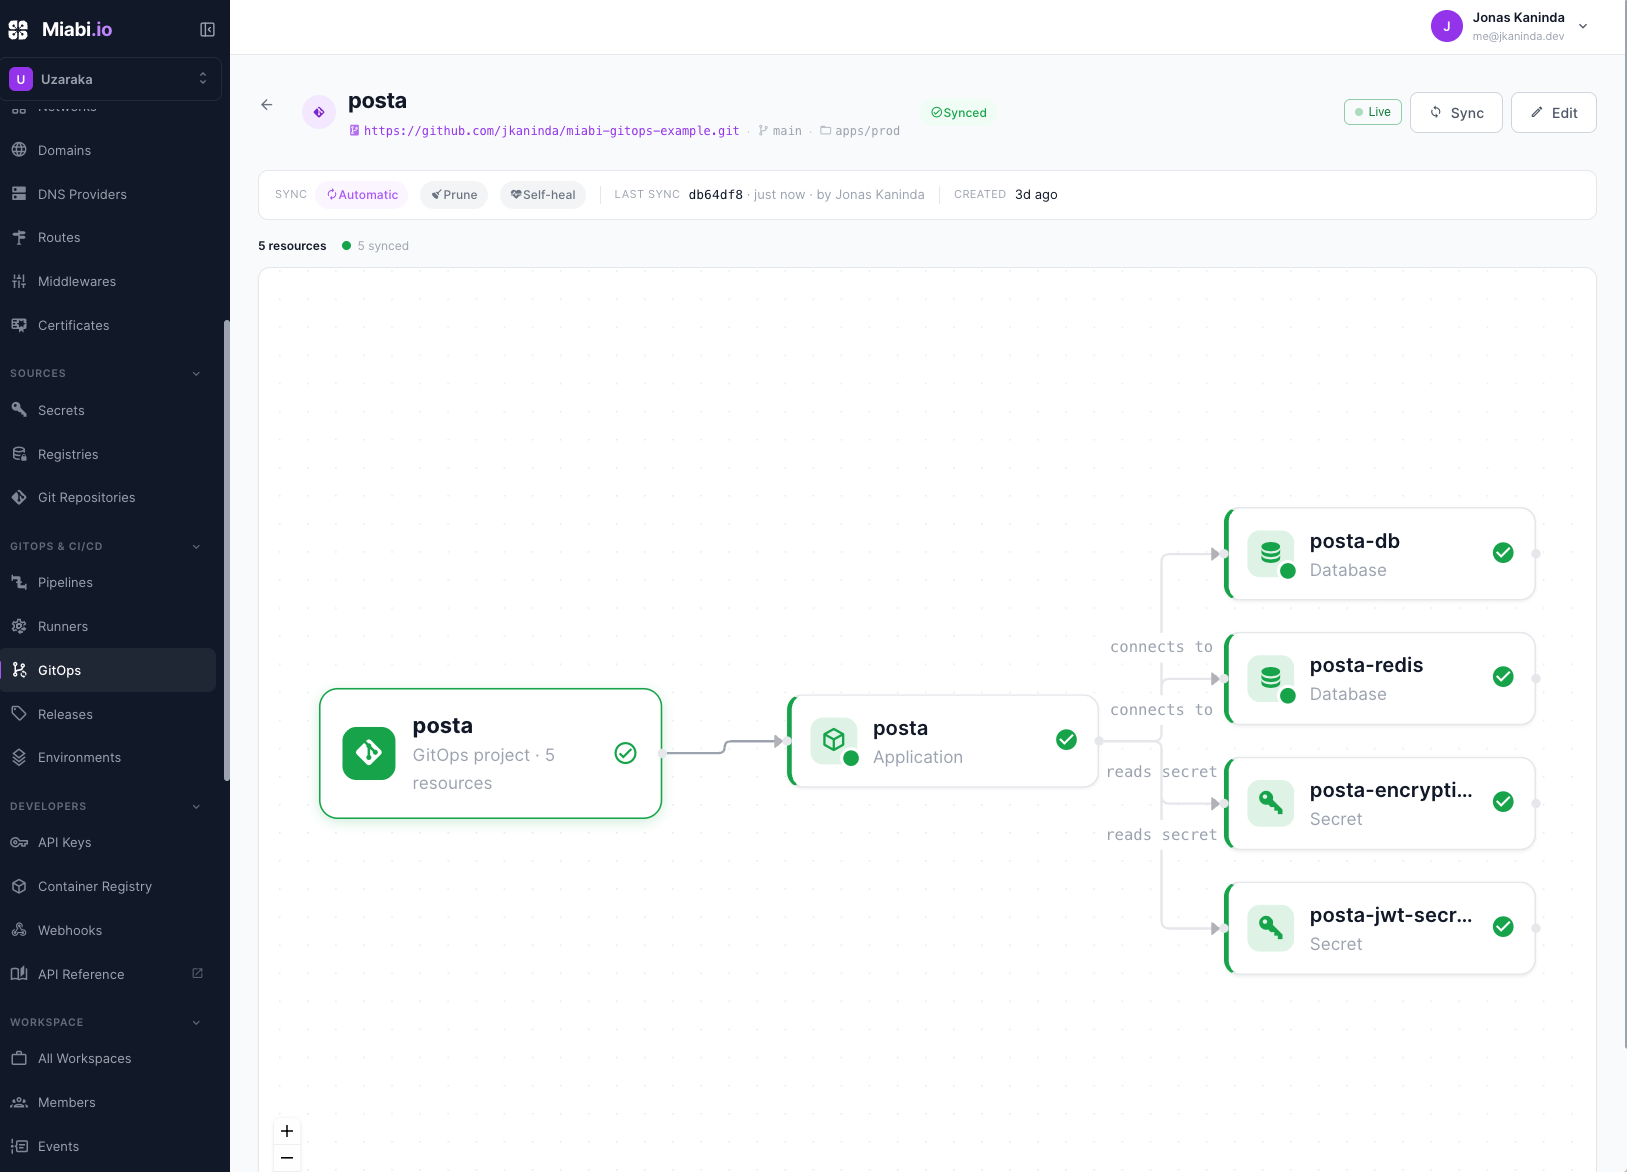 |
Analytics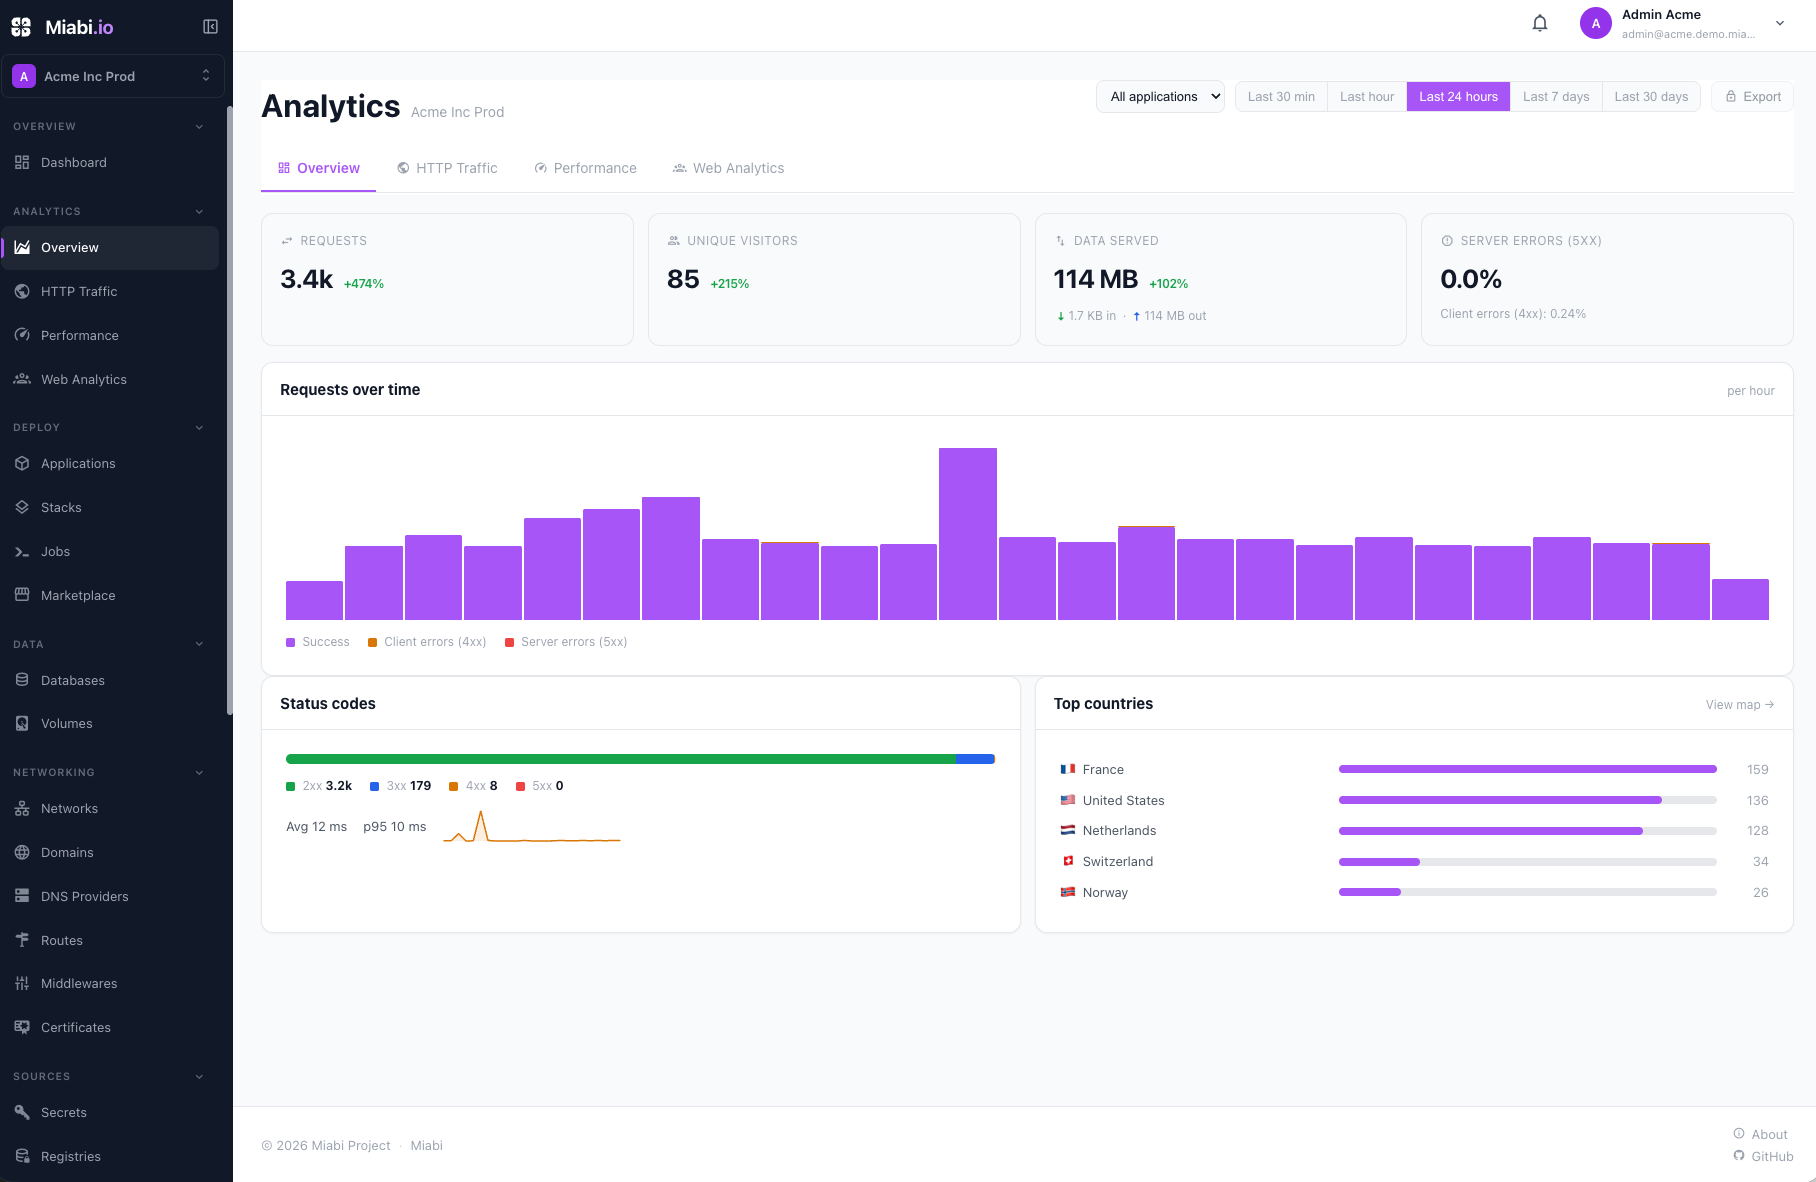 |
Nodes & cluster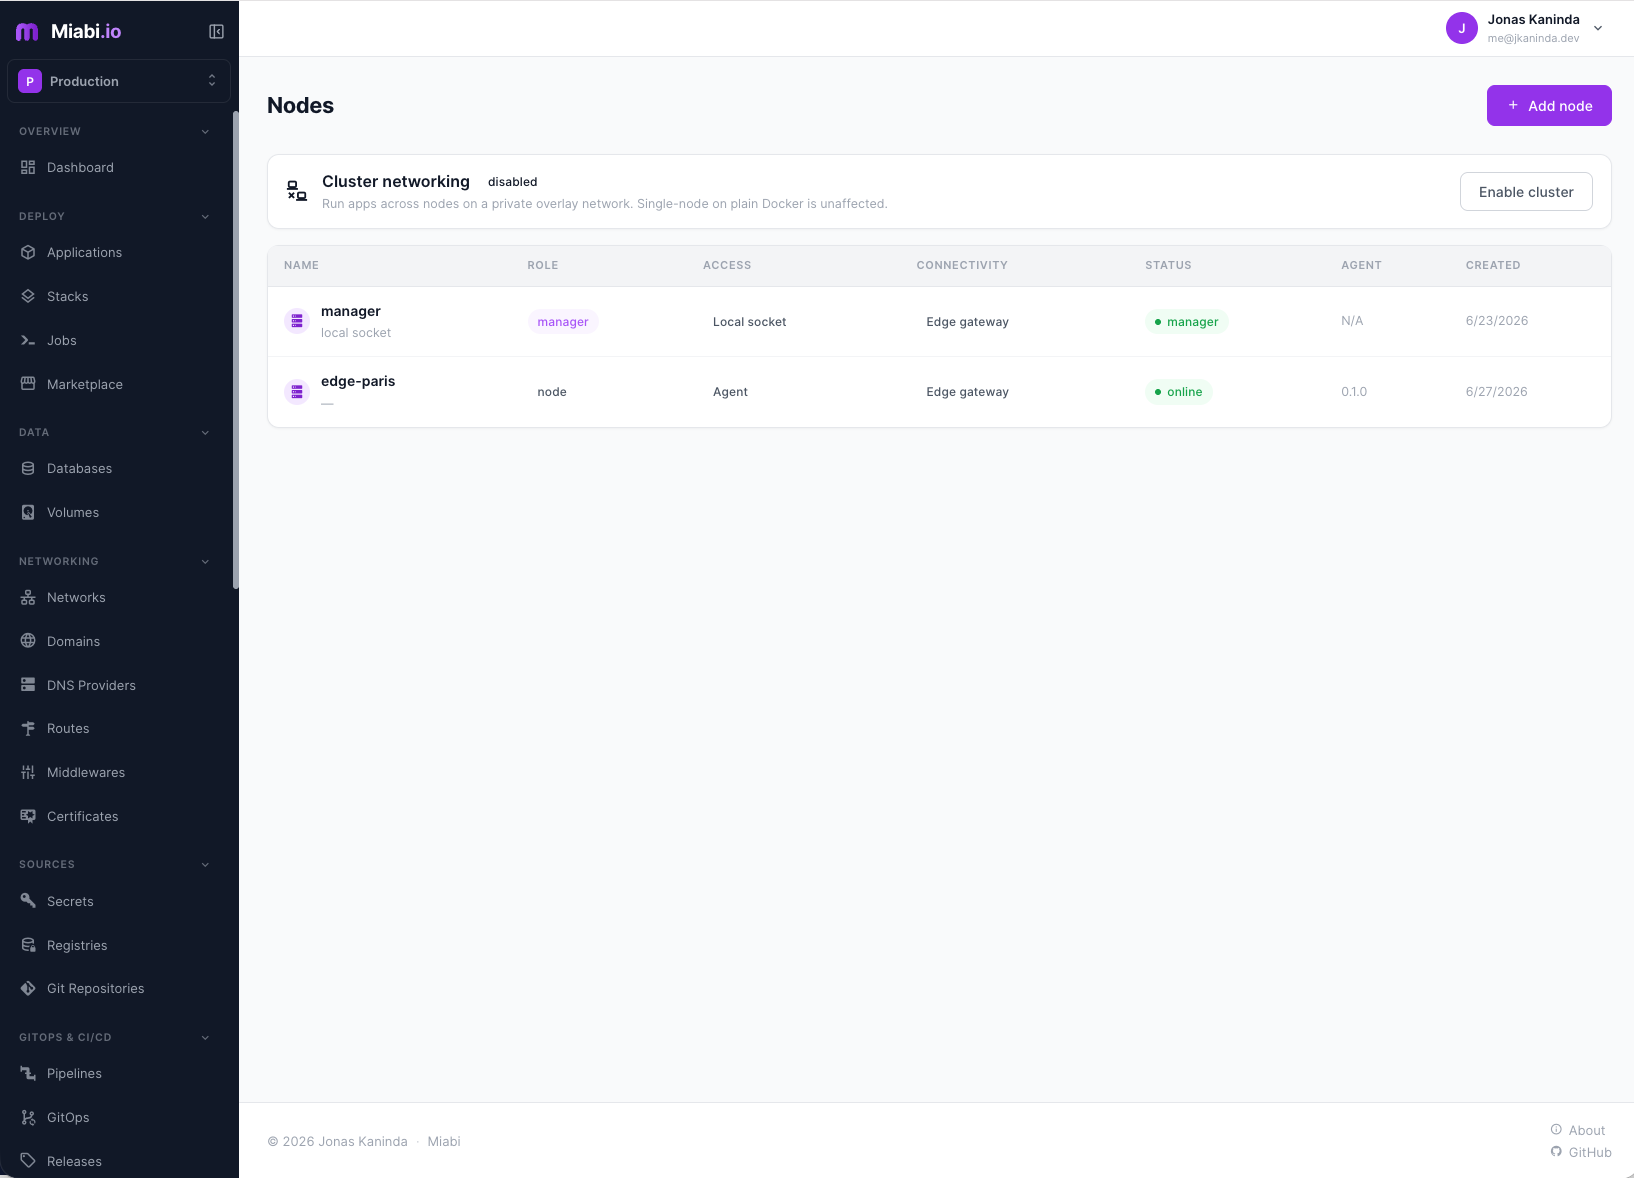 |
Managed databases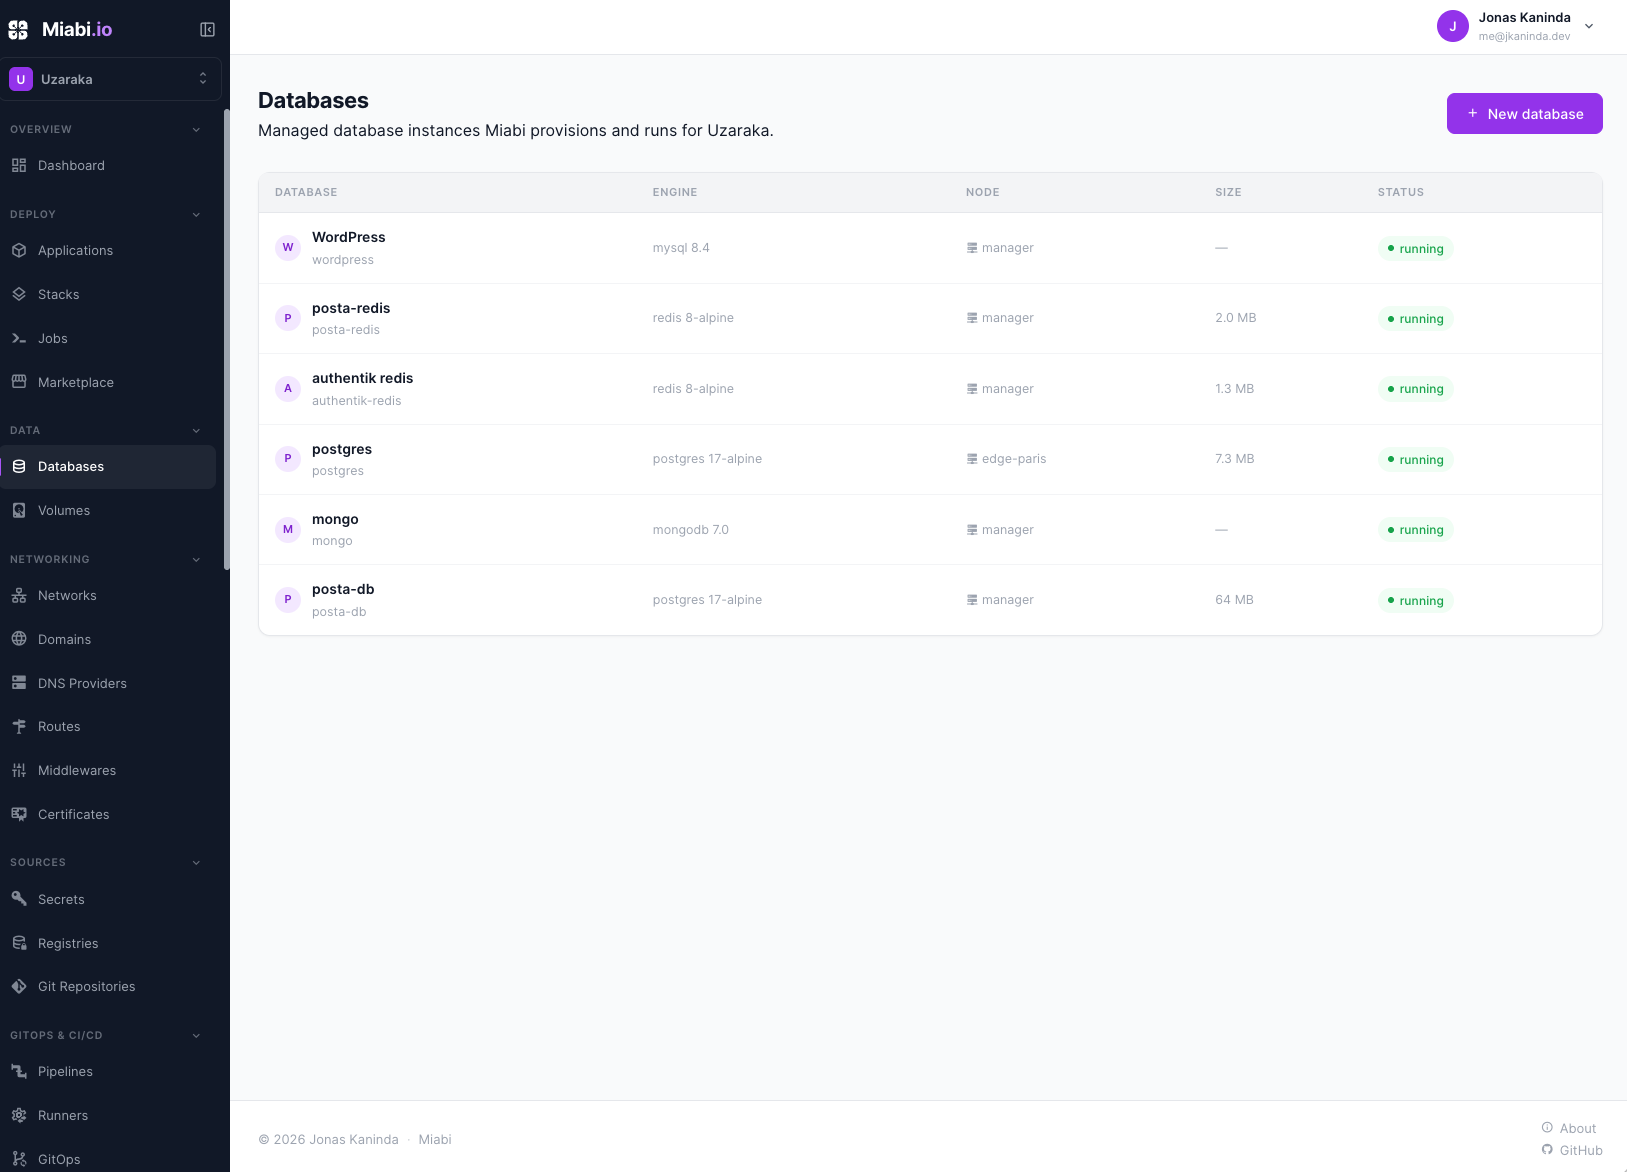 |
More screenshots — pipelines, domains, backups, monitoring, marketplace, admin
CI/CD pipelines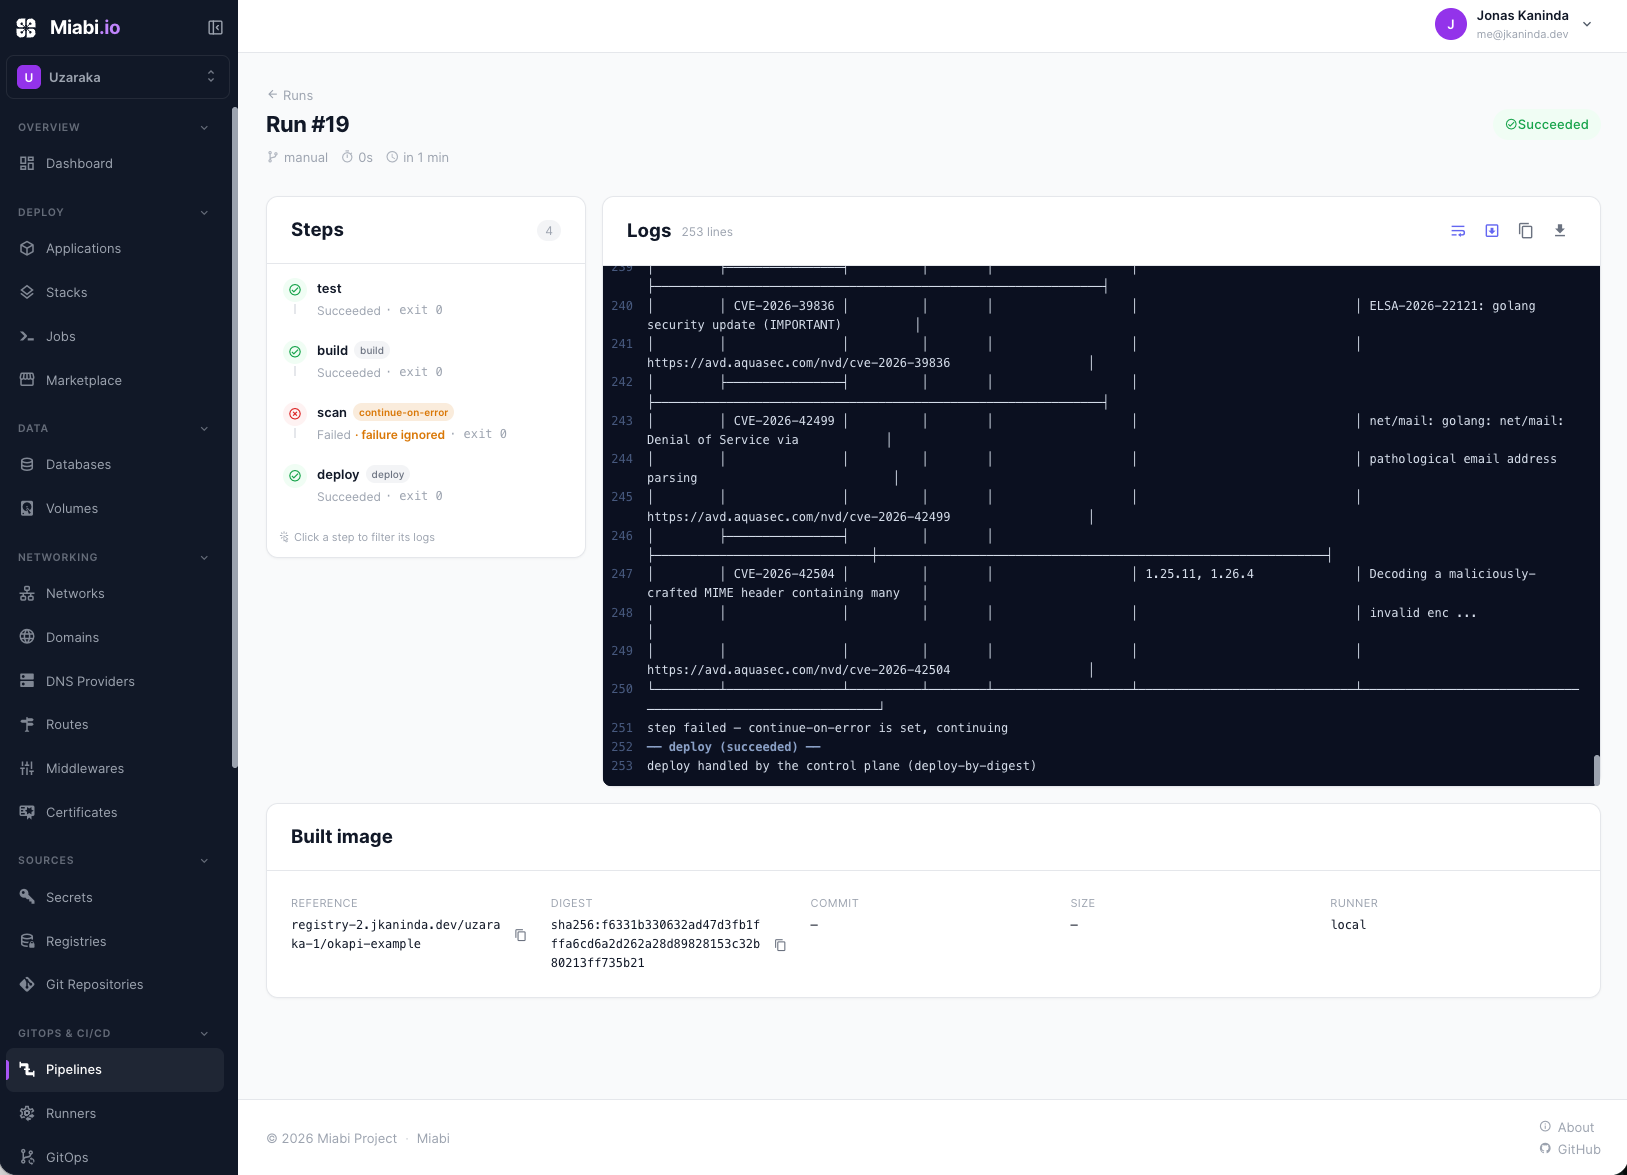 |
Domains, routes & TLS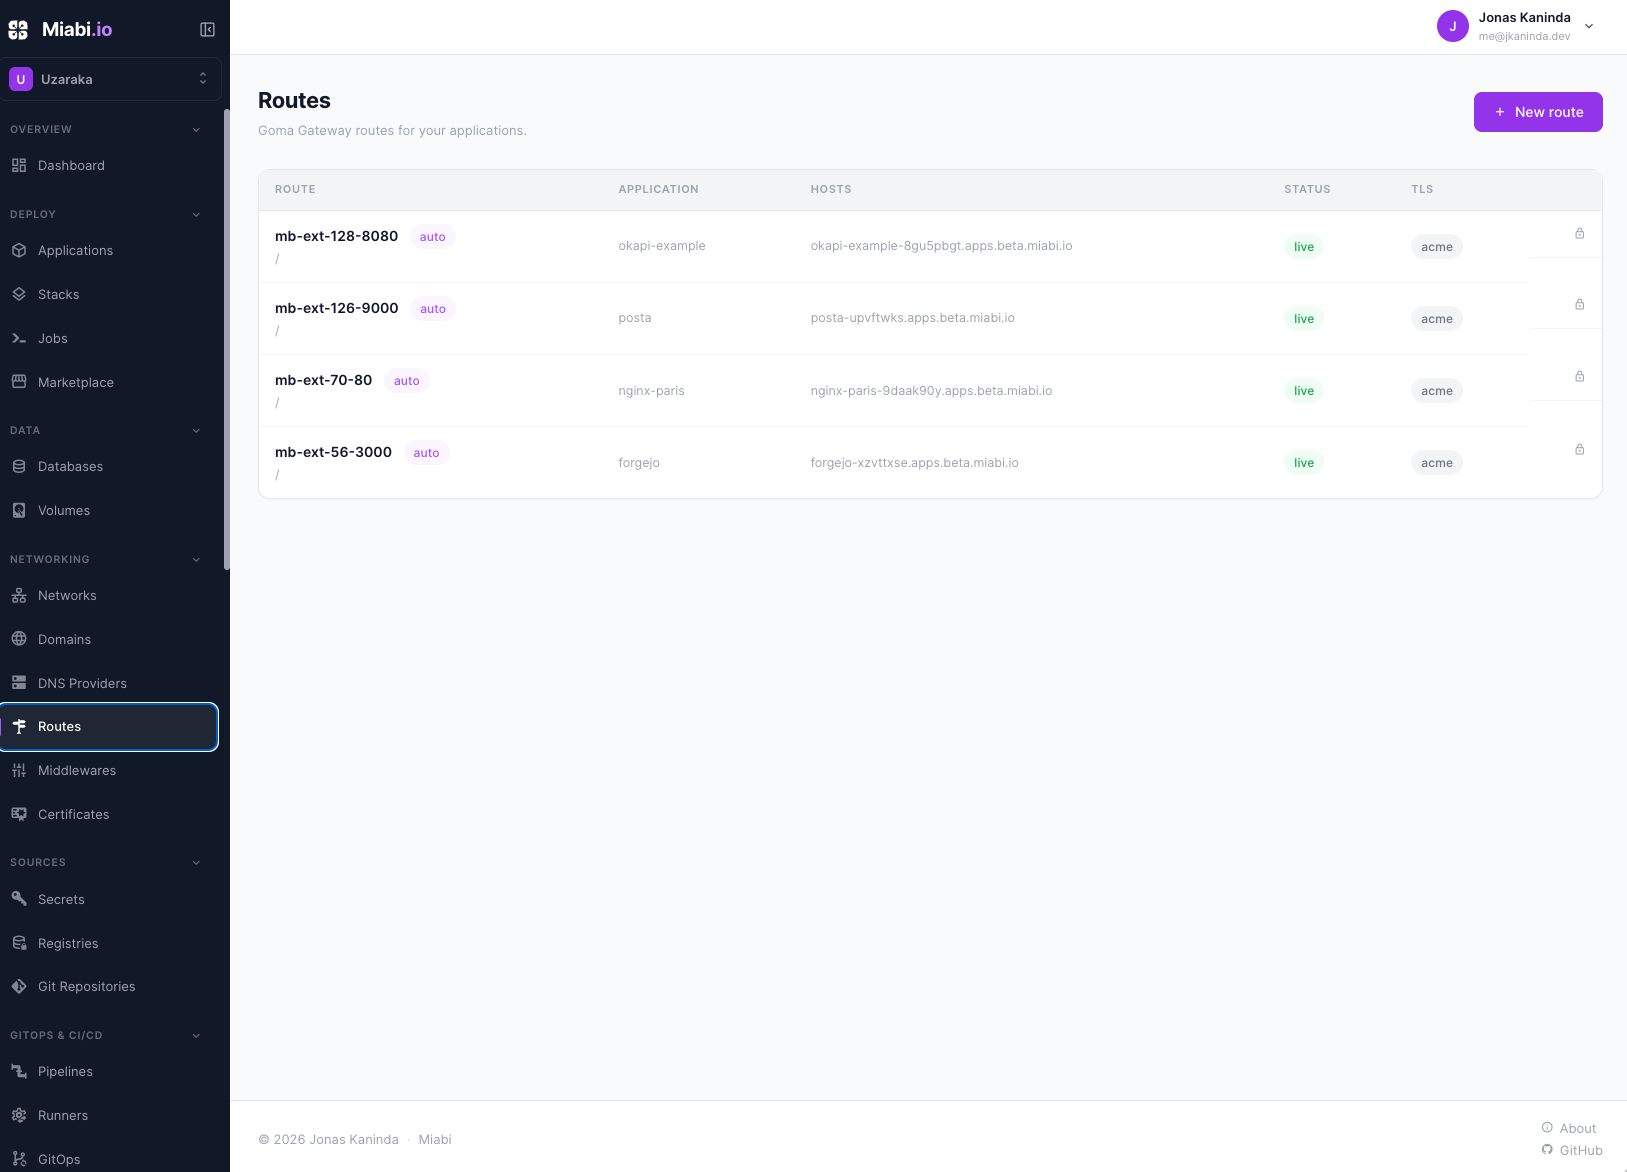 |
Backups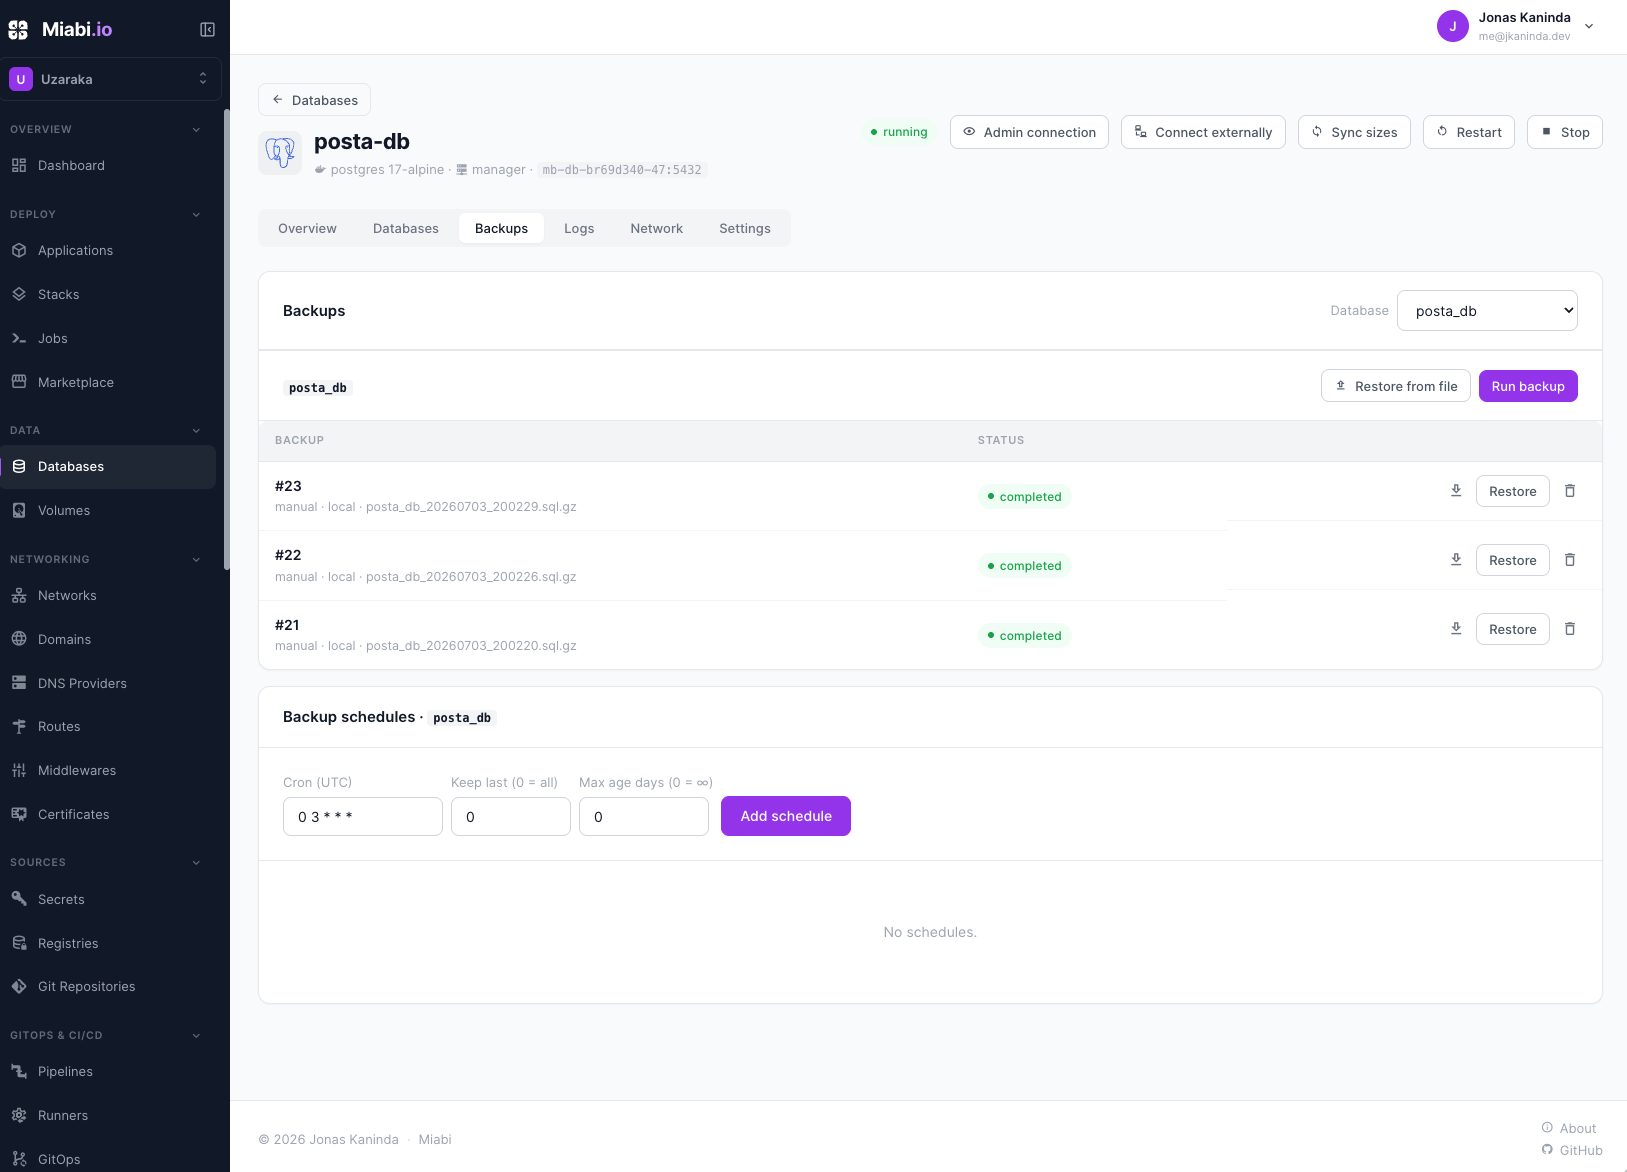 |
Monitoring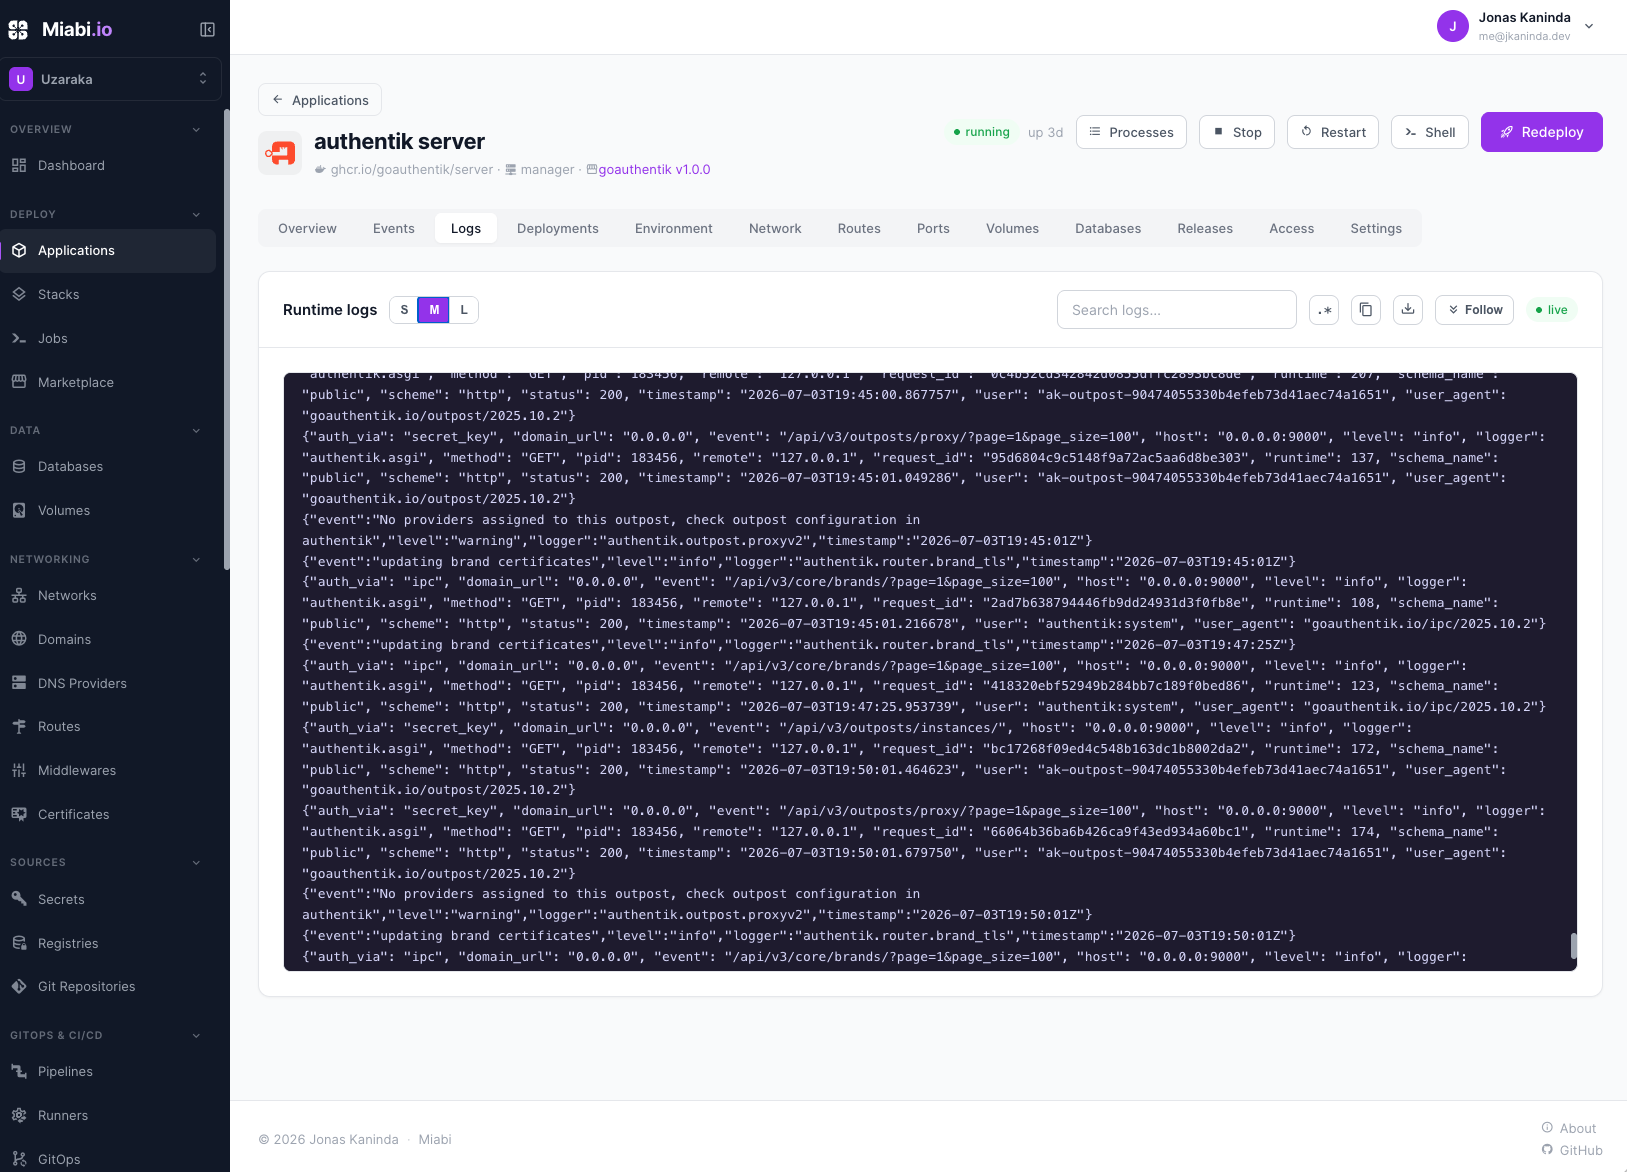 |
Marketplace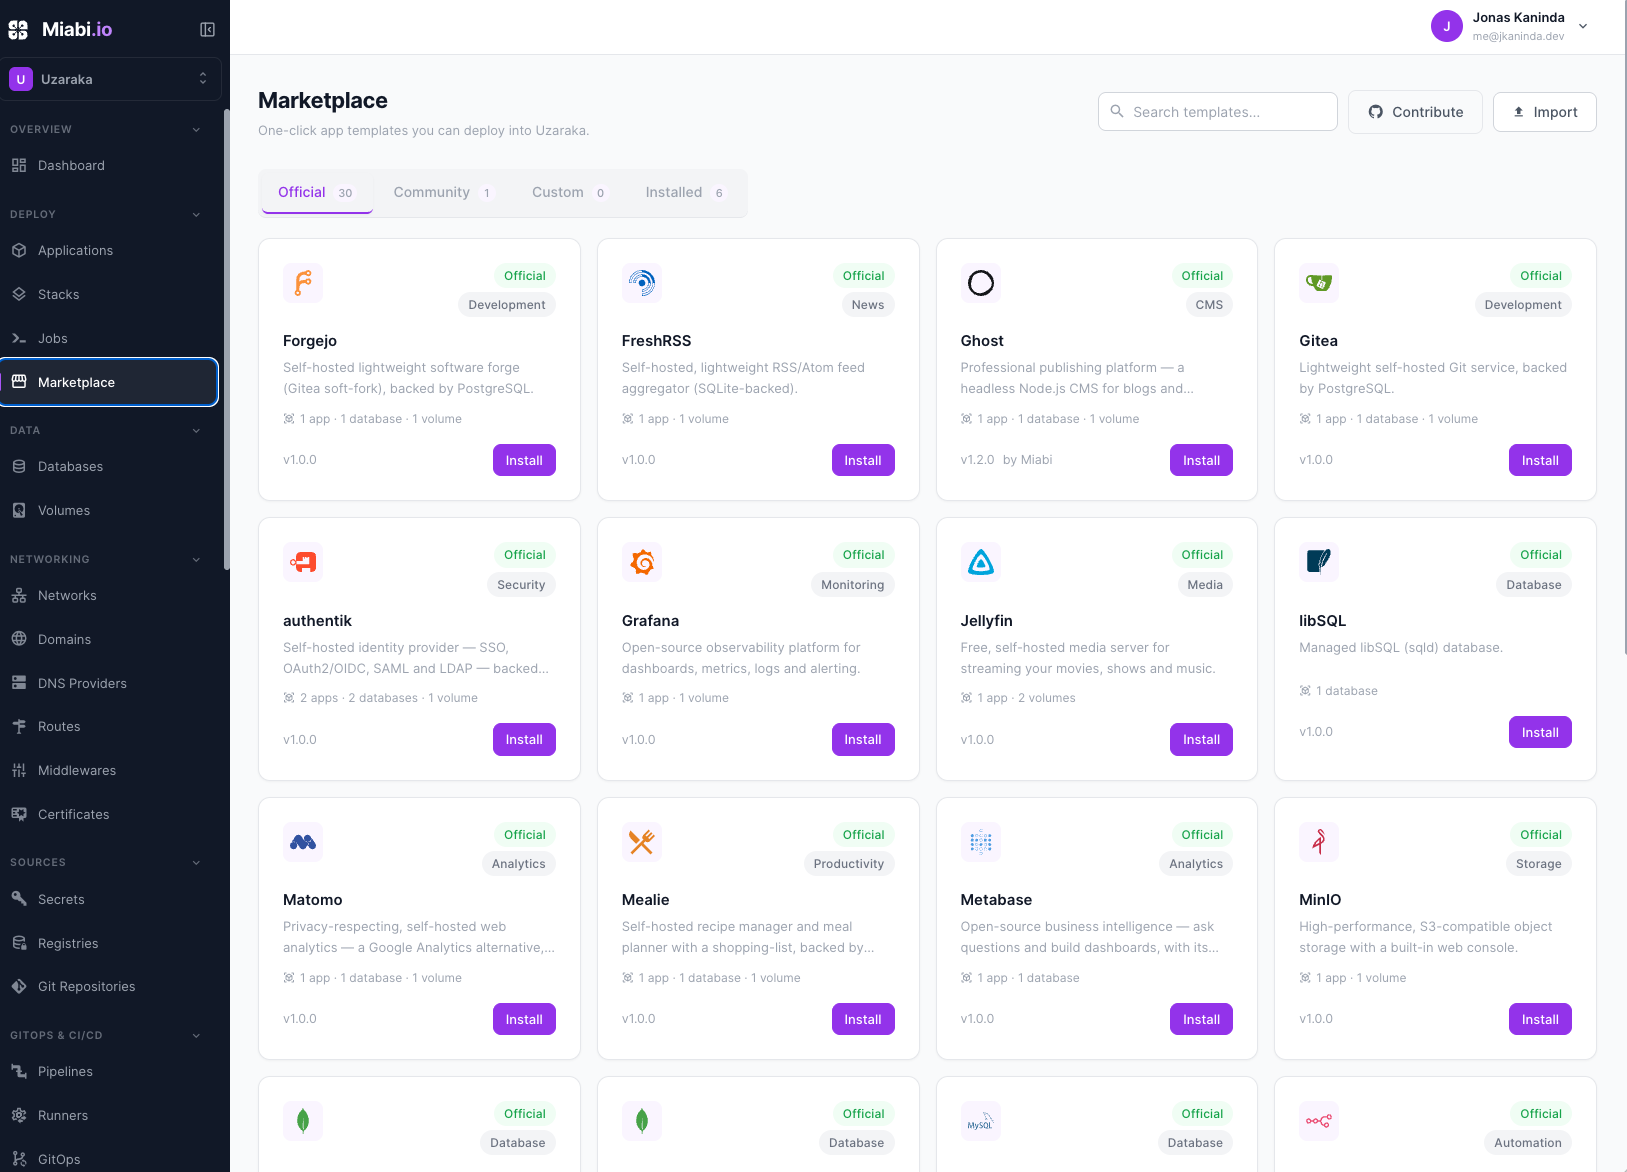 |
Platform admin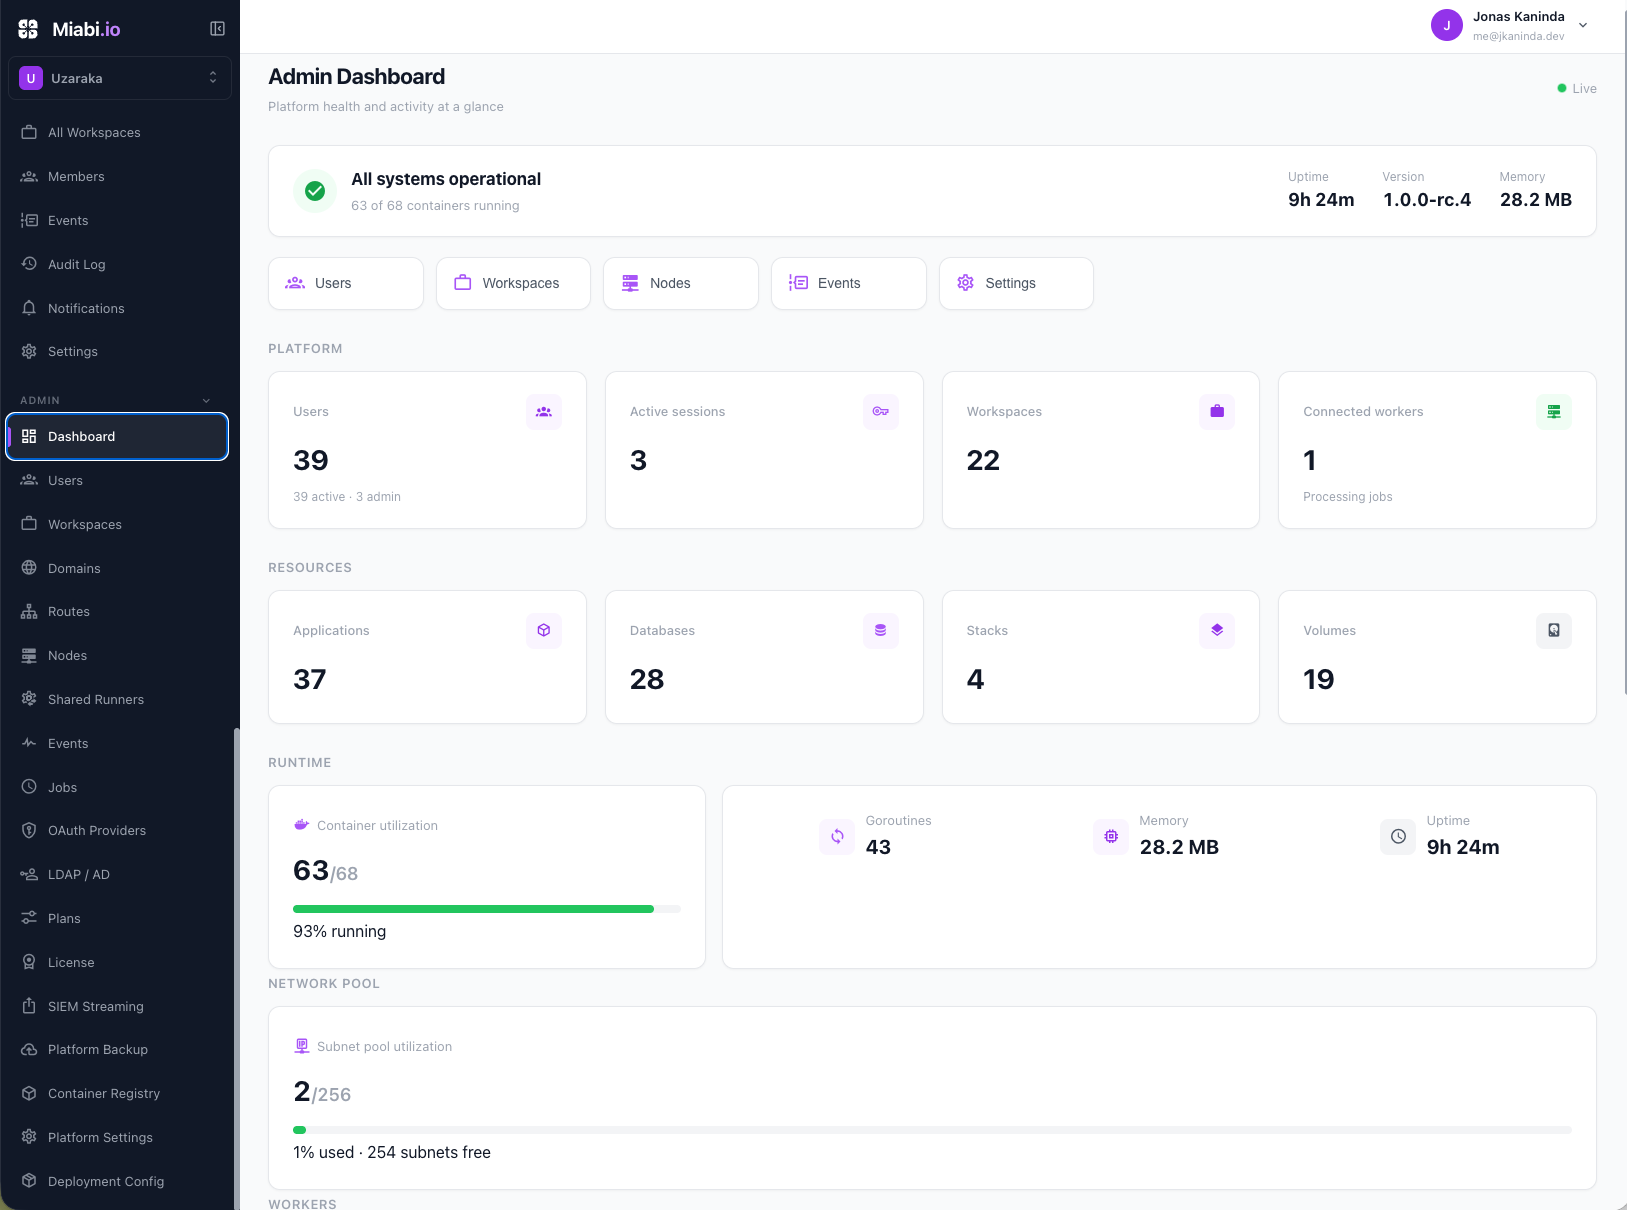 |
Application overview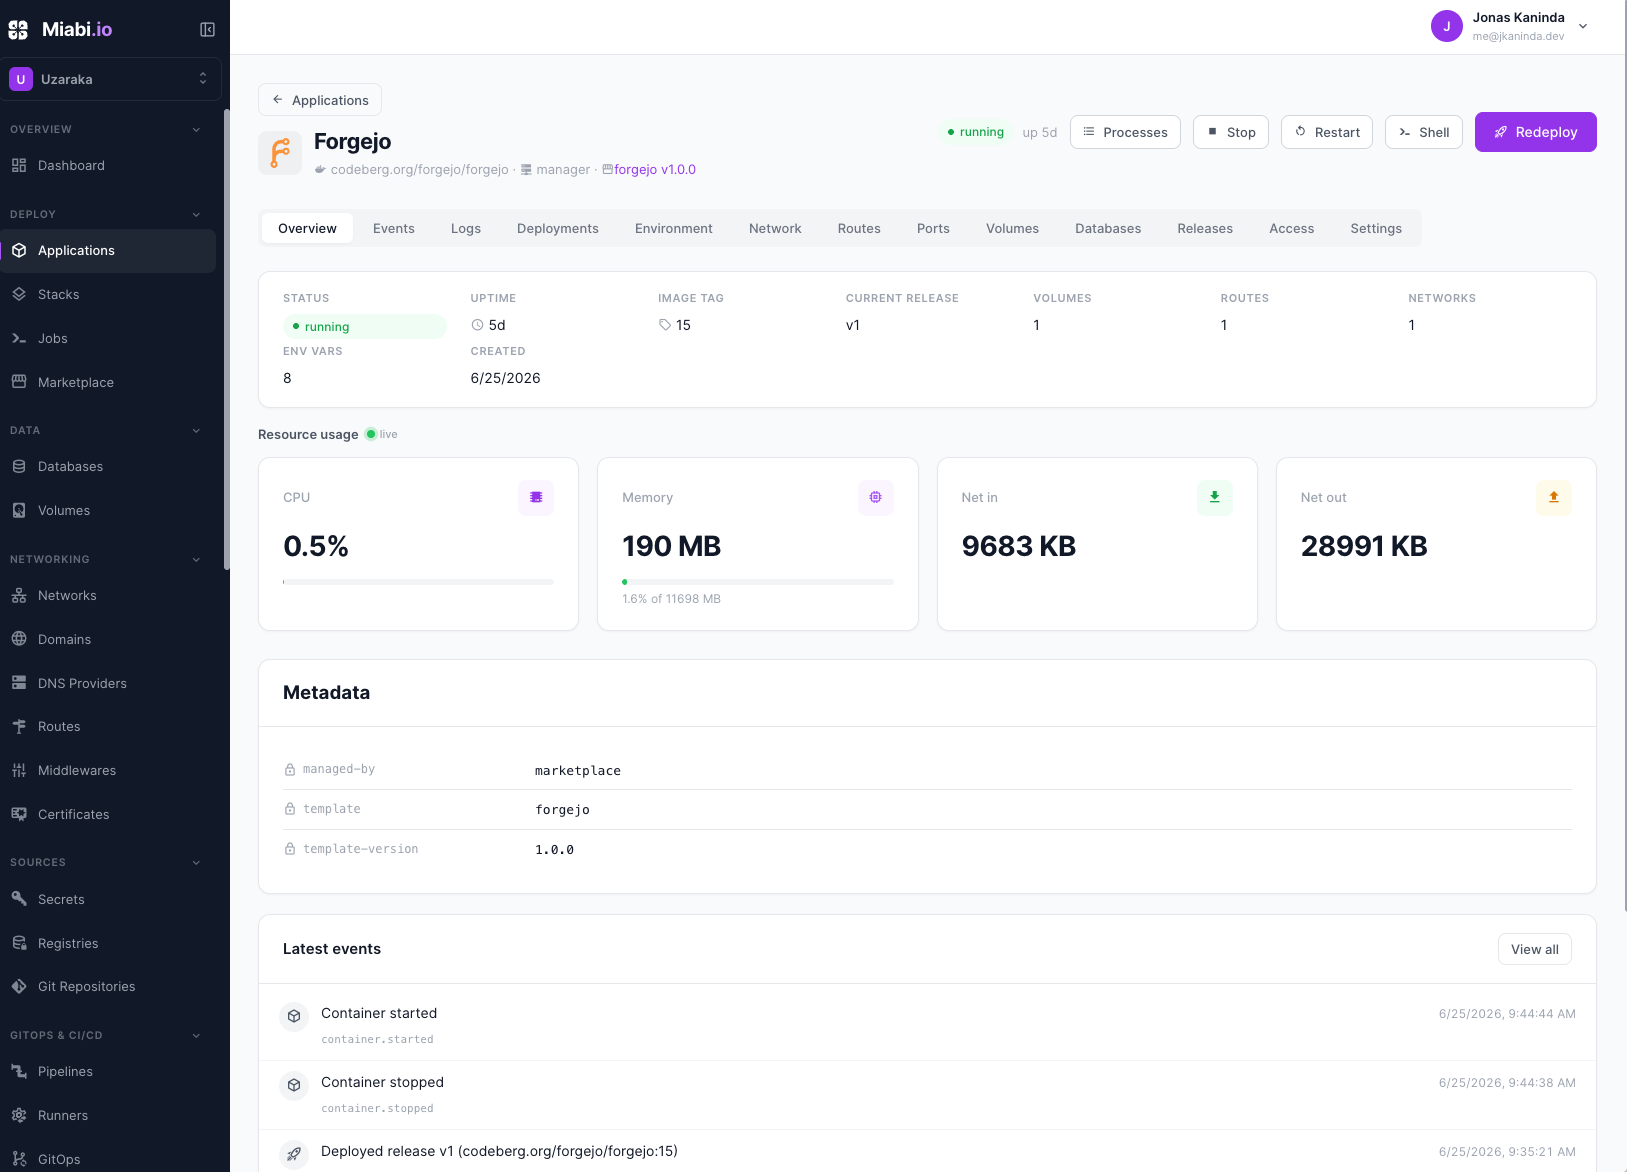 |
HTTP traffic analytics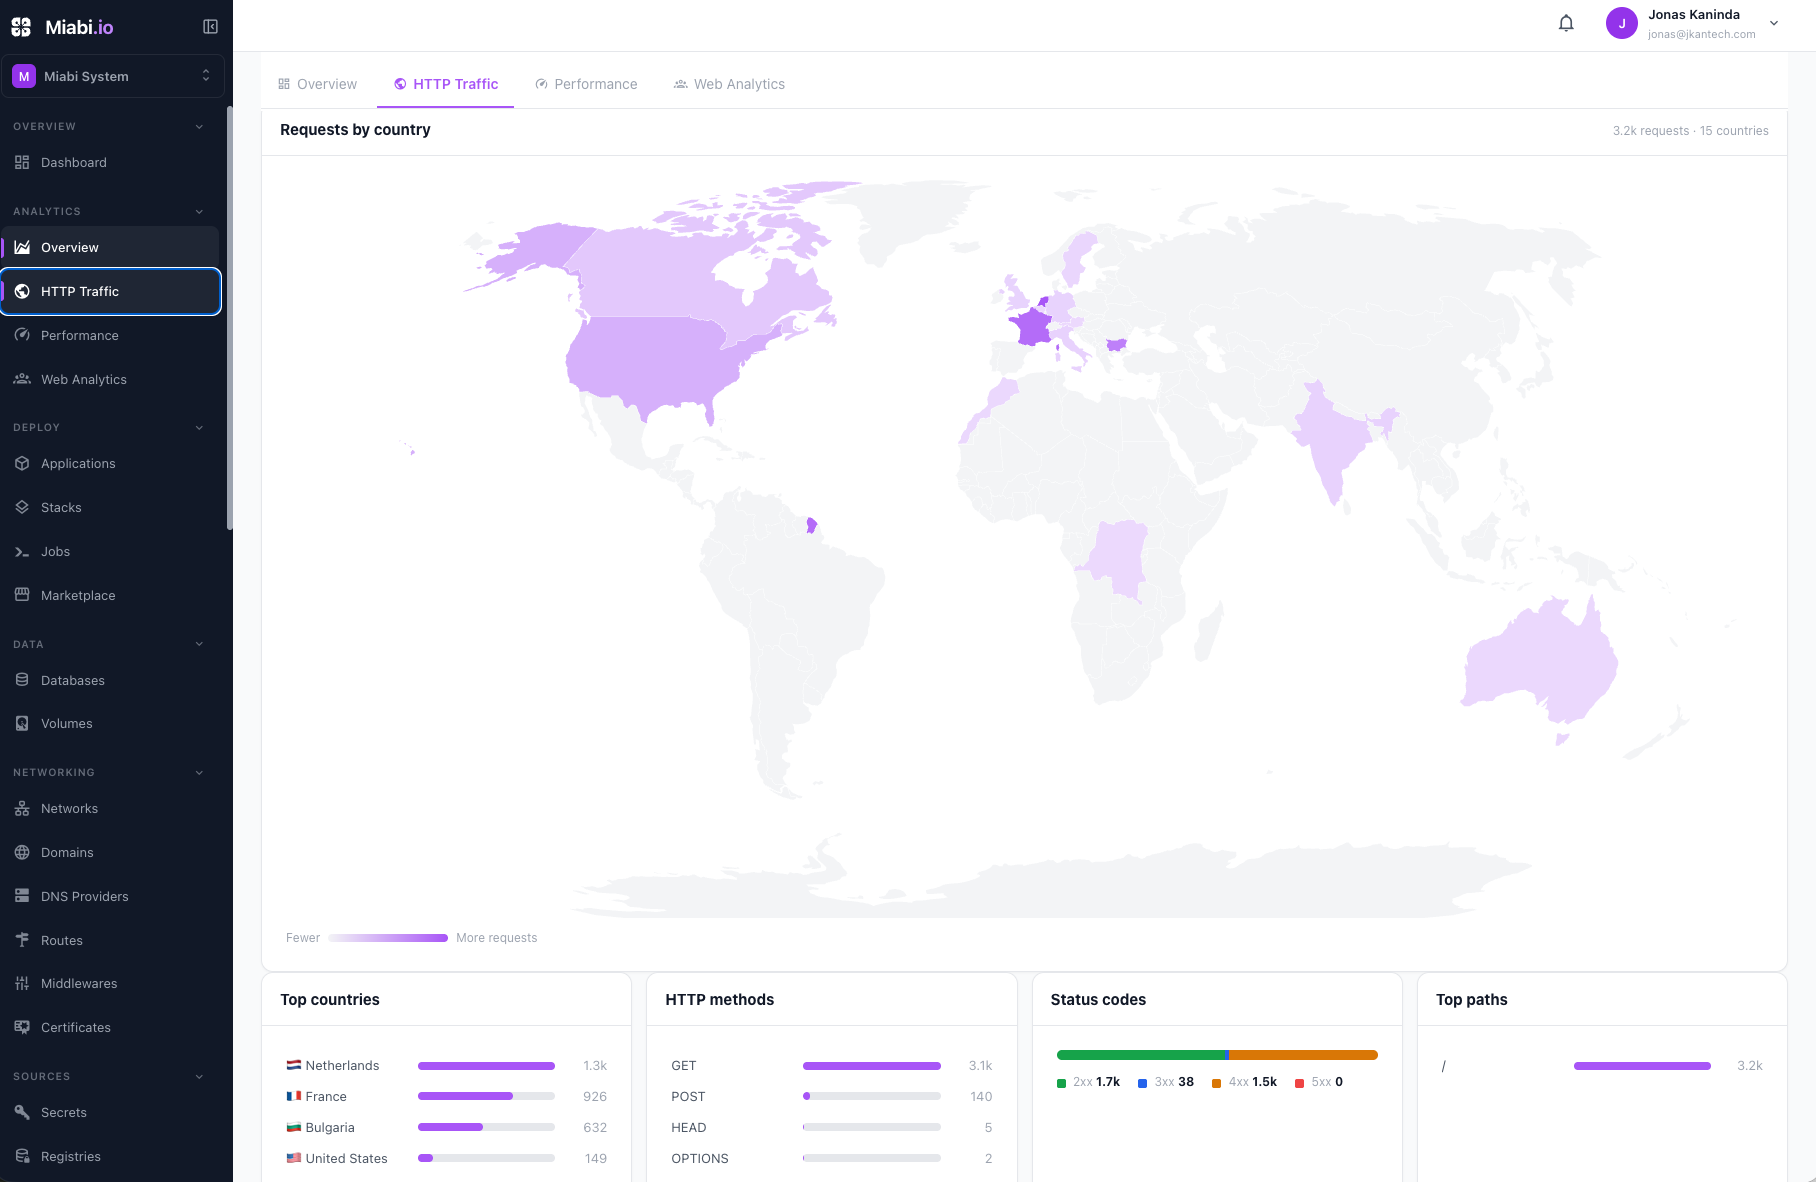 |
How Miabi compares
All four projects are self-hosted, open source, and deploy from Git or a Docker image with automatic HTTPS. The table covers only where they differ.
| Feature | Miabi | Coolify | Dokploy | CapRover |
|---|---|---|---|---|
| Multi-tenancy & workspace isolation | ✅ | ❌ | ❌ | ❌ |
| Organizations, teams & RBAC | ✅ | Limited | ❌ | ❌ |
| Shared hosting | ✅ | ❌ | ❌ | ❌ |
| Canary deployments | ✅ | ❌ | ❌ | ❌ |
| Zero-downtime deployments | ✅ | Limited | Limited | Limited |
| Built-in CI/CD pipelines | ✅ | ❌ | ❌ | ❌ |
| GitOps (no extra controller) | ✅ | ❌ | ❌ | ❌ |
| Built-in container registry | ✅ | ❌ | ❌ | ❌ |
| Built-in analytics (privacy-first) | ✅ | ❌ | ❌ | ❌ |
| Audit logs | ✅ | ❌ | ❌ | ❌ |
| OpenAPI-documented REST API | ✅ | ❌ | Partial | Limited |
| Official CLI | ✅ | ❌ | ❌ | ❌ |
| Terraform provider | ✅ | ❌ | ❌ | ❌ |
| Multi-node deployments | ✅ | Partial | Partial | Partial |
| Docker import (adopt existing containers) | ✅ | ❌ | ❌ | ❌ |
| Scheduled backups | ✅ | Partial | Partial | ❌ |
| SAML / LDAP | ✅ (Enterprise) | ❌ | ❌ | ❌ |
Compiled from each project's public documentation. These projects move fast — if something here is out of date, please open a PR and we'll correct it.
Architecture
Browser / CLI / API clients
        │
        ▼
Goma Gateway (routing, TLS/ACME)
        │
        ▼
Miabi control plane (single Go binary: REST API + embedded Vue console)
        │
        ├─ asynq worker ── deploys, provisioning, backups
        ├─ PostgreSQL (GORM) · Redis (cache/queue)
        │
        ▼
Clusters (Docker Engine, optional Swarm per cluster)
        ├─ default cluster ── local socket, plus its Swarm members
        ├─ standalone nodes ── outbound agent tunnel, own edge gateway
        └─ remote Swarm clusters ── managers via agent tunnel, own ingress gateway
| Layer | Technology |
|---|---|
| Backend | Go 1.25+, Okapi framework, REST + OpenAPI |
| Frontend | Vue 3 + Pinia + Vite, built and statically served by the binary |
| Database | PostgreSQL (GORM) |
| Queue / cache | Redis + Asynq |
| Runtime | Docker Engine 25+ via the Moby SDK for Go (moby/moby/client), optional Swarm |
| Reverse proxy / TLS | Goma Gateway |
| Metrics | Prometheus |
The console source lives in web/ and is embedded into the Go binary, so a deployment is a single image. The node agent is a separate module, github.com/miabi-io/agent: a thin Docker proxy that needs only an outbound connection and the local Docker socket.
Live Demo
Try Miabi without installing anything at https://demo.miabi.io (password for all accounts: MiabiDemo2026).
The demo is seeded with two independent customers across three workspaces, so the core idea is visible immediately: shared hosting on Docker with true workspace isolation and role-based access. Every app, database, domain, volume, and secret belongs to a workspace; one tenant can never see or reach another's resources; a member only sees what their role grants.
| Sign in as | Workspaces | Role | Represents |
|---|---|---|---|
admin@acme.demo.miabi.io |
Acme Inc Prod · Acme Inc Dev | Owner | one org running prod and dev in separate, isolated workspaces |
dev@acme.demo.miabi.io |
Acme Inc Dev | Developer | a teammate scoped to a single workspace — can't see Acme Inc Prod |
admin@startup.demo.miabi.io |
Startup Prod | Owner | a different tenant — invisible to Acme |
Switch workspaces from the picker to watch the console re-scope, then sign in as the other customer to confirm the isolation boundary.
[!IMPORTANT] These are workspace accounts, not the platform admin. They can't reach the admin platform (nodes/cluster, users, plans, settings, licensing). To explore platform-admin features, install Miabi — the first account you seed is the platform admin.
[!NOTE] Demo apps run under a restricted (non-root) security profile: each container runs as a dedicated unprivileged user. If you deploy an app, make sure its image can run as non-root, or it will fail to start.
Development
Building from source needs Go 1.25+, Node (for the console), a PostgreSQL and a Redis instance, and a reachable Docker socket.
git clone https://github.com/miabi-io/miabi.git
cd miabi

make run        # API server on :9000, worker embedded
make worker     # standalone background worker (optional)
make build-ui   # build the Vue console into the embedded assets
make test       # unit + integration tests
The OpenAPI spec is generated from code annotations in internal/routes/ and served at /docs and /openapi.json on any running instance.
Ecosystem
Miabi is part of a family of self-hosting tools by the same author:
| Project | What it is |
|---|---|
| Okapi | The Go web framework Miabi is built on |
| Goma Gateway | Reverse proxy with TLS/ACME |
| cli | The official CLI |
| terraform-provider-miabi | Terraform / OpenTofu provider |
| agent | Outbound node agent for multi-node |
| runner | Dedicated build and pipeline runner |
| marketplace | Official app template catalog |
| Posta | Self-hosted email delivery and inbound |
| pg-bkup / mysql-bkup | Database backup tools |
Support & contributing
- Docs — https://docs.miabi.io
- Questions & ideas — GitHub Discussions
- Bugs & features — open an issue. Please open one before submitting a pull request, so the approach can be agreed first
- Security — report vulnerabilities privately to maintainers@miabi.io. Please don't file public issues for security problems
If Miabi is useful to you, starring the repo genuinely helps other people find it.
License
| Path | License |
|---|---|
| Core | AGPL-3.0-or-later — LICENSE, NOTICE |
pkg/ |
Apache-2.0 — pkg/LICENSE |
internal/enterprise/ |
Miabi Enterprise License — LICENSE.md |
The reusable packages under pkg/ are the importable half of the project (pkg/stack is the host installer and lifecycle engine the CLI drives), so embedding them carries no AGPL obligation — nothing under pkg/ depends on AGPL-licensed code.
Enterprise features are built with the enterprise tag and require a valid commercial license.LICENSING.md has the full breakdown.
Copyright © 2026 Jonas Kaninda
 Directories

| Path | Synopsis |
|---|---|
|
cmd
|
|
|
miabi
command
|
|
|
mwdocsgen
command
Command mwdocsgen writes the middleware reference pages for the documentation site from the middleware catalog.
|
Command mwdocsgen writes the middleware reference pages for the documentation site from the middleware catalog. |
|
schemagen
command
Command schemagen renders the miabi.io/v1 JSON Schema from the types the manifest parser binds to.
|
Command schemagen renders the miabi.io/v1 JSON Schema from the types the manifest parser binds to. |
|
internal
|
|
|
acme
Package acme issues TLS certificates via ACME DNS-01, backed by go-acme/lego.
|
Package acme issues TLS certificates via ACME DNS-01, backed by go-acme/lego. |
|
cron
Package cron is a generic recurring-task scheduler over robfig/cron.
|
Package cron is a generic recurring-task scheduler over robfig/cron. |
|
datavolume
Package datavolume refuses to start a workload whose data is gone.
|
Package datavolume refuses to start a workload whose data is gone. |
|
dbenvelope
Package dbenvelope seals the data key that encrypts a database recovery point.
|
Package dbenvelope seals the data key that encrypts a database recovery point. |
|
declarative
Package declarative is the shared declarative resource model for Miabi: a family of miabi.io/v1 kinds with one parse/validate/render path and one plan/diff engine.
|
Package declarative is the shared declarative resource model for Miabi: a family of miabi.io/v1 kinds with one parse/validate/render path and one plan/diff engine. |
|
dns
Package dns abstracts a managed DNS host behind one small Provider interface, backed by libdns modules.
|
Package dns abstracts a managed DNS host behind one small Provider interface, backed by libdns modules. |
|
dnscatalog
Package dnscatalog is the single source of truth for the DNS hosts Miabi can connect to.
|
Package dnscatalog is the single source of truth for the DNS hosts Miabi can connect to. |
|
dnscatalog/gen
command
Command gen prints the supported-providers table for the docs, so the page cannot drift from the catalog.
|
Command gen prints the supported-providers table for the docs, so the page cannot drift from the catalog. |
|
docker
Package docker is the sole adapter over the Docker Engine SDK.
|
Package docker is the sole adapter over the Docker Engine SDK. |
|
dotenv
Package dotenv parses .env-style KEY=VALUE text into ordered pairs, for bulk importing application and stack environment variables.
|
Package dotenv parses .env-style KEY=VALUE text into ordered pairs, for bulk importing application and stack environment variables. |
|
dr
Package dr holds the disaster-recovery primitives shared by the running platform and the host-side `miabi restore`: the sealed identity envelope and the naming of a recovery point's artifacts.
|
Package dr holds the disaster-recovery primitives shared by the running platform and the host-side `miabi restore`: the sealed identity envelope and the naming of a recovery point's artifacts. |
|
drift
Package drift is the shared vocabulary for divergence between what Miabi recorded and what Docker runs.
|
Package drift is the shared vocabulary for divergence between what Miabi recorded and what Docker runs. |
|
hostmount
Package hostmount defines the fixed, allow-listed set of host bind mounts a privileged workspace may attach to a container.
|
Package hostmount defines the fixed, allow-listed set of host bind mounts a privileged workspace may attach to a container. |
|
hoststats
Package hoststats reads real host CPU and memory usage from a procfs directory.
|
Package hoststats reads real host CPU and memory usage from a procfs directory. |
|
leader
Package leader elects the one process that runs the control plane's singleton work: scheduled jobs, periodic scans and cluster reconciliation.
|
Package leader elects the one process that runs the control plane's singleton work: scheduled jobs, periodic scans and cluster reconciliation. |
|
logstore
Package logstore is the shared store for execution logs.
|
Package logstore is the shared store for execution logs. |
|
metrics
Package metrics exposes Prometheus collectors and the /metrics handler.
|
Package metrics exposes Prometheus collectors and the /metrics handler. |
|
middlewares
Package middlewares holds HTTP middleware: authentication, workspace scoping, and role-based access control.
|
Package middlewares holds HTTP middleware: authentication, workspace scoping, and role-based access control. |
|
mwcatalog
Package mwcatalog is the single source of truth for the curated Goma middleware types Miabi exposes as security policies.
|
Package mwcatalog is the single source of truth for the curated Goma middleware types Miabi exposes as security policies. |
|
netguard
Package netguard provides SSRF-resistant HTTP clients for outbound requests to user-supplied URLs.
|
Package netguard provides SSRF-resistant HTTP clients for outbound requests to user-supplied URLs. |
|
nodes
Package nodes manages the control plane's view of cluster nodes: the per-node Docker client registry and the agent connection manager.
|
Package nodes manages the control plane's view of cluster nodes: the per-node Docker client registry and the agent connection manager. |
|
proxy
Package proxy abstracts the reverse proxy / gateway (Goma Gateway).
|
Package proxy abstracts the reverse proxy / gateway (Goma Gateway). |
|
runners
Package runners maintains the live tunnels of connected build/pipeline runners.
|
Package runners maintains the live tunnels of connected build/pipeline runners. |
|
services/account
Package account orchestrates account-wide actions across a user's owned workspaces: stopping every app and database when an account is disabled, and cascade-deleting a user's data on removal.
|
Package account orchestrates account-wide actions across a user's owned workspaces: stopping every app and database when an account is disabled, and cascade-deleting a user's data on removal. |
|
services/analytics
Package analytics turns Goma Gateway's per-request event stream into minute-bucketed rollups and answers the Traffic, Performance and Web Analytics queries over them.
|
Package analytics turns Goma Gateway's per-request event stream into minute-bucketed rollups and answers the Traffic, Performance and Web Analytics queries over them. |
|
services/announcement
Package announcement broadcasts platform notices into per-user inboxes.
|
Package announcement broadcasts platform notices into per-user inboxes. |
|
services/application
Package application manages applications, their config, and deployments.
|
Package application manages applications, their config, and deployments. |
|
services/apply
Package apply is the imperative, one-shot sibling of GitOps: it turns a bundle of miabi.io/v1 manifests into a plan or converges the workspace to them, by diffing desired state against a live snapshot and driving the existing services.
|
Package apply is the imperative, one-shot sibling of GitOps: it turns a bundle of miabi.io/v1 manifests into a plan or converges the workspace to them, by diffing desired state against a live snapshot and driving the existing services. |
|
services/audit
Package audit writes append-only audit-log entries for mutating actions.
|
Package audit writes append-only audit-log entries for mutating actions. |
|
services/auth
Package auth handles user authentication: password hashing, JWT issuance with revocable sessions, and password resets.
|
Package auth handles user authentication: password hashing, JWT issuance with revocable sessions, and password resets. |
|
services/backup
Package backup runs database backups and restores using the ecosystem pg-bkup / mysql-bkup tools as one-shot containers, to a per-workspace backup volume (local) or an S3-compatible bucket.
|
Package backup runs database backups and restores using the ecosystem pg-bkup / mysql-bkup tools as one-shot containers, to a per-workspace backup volume (local) or an S3-compatible bucket. |
|
services/backupsettings
Package backupsettings manages a workspace's shared S3 backup target: the single bucket + credentials and the database/volume path prefixes that both database and volume backups draw from.
|
Package backupsettings manages a workspace's shared S3 backup target: the single bucket + credentials and the database/volume path prefixes that both database and volume backups draw from. |
|
services/branding
Package branding owns the operator's identity: the name, logos, favicon, accent, sign-in notice and links shown on the sign-in page and in the console chrome, and whether accounts may pick an accent of their own.
|
Package branding owns the operator's identity: the name, logos, favicon, accent, sign-in notice and links shown on the sign-in page and in the console chrome, and whether accounts may pick an accent of their own. |
|
services/certificate
Package certificate manages workspace-scoped imported TLS certificates; ACME is handled by Goma.
|
Package certificate manages workspace-scoped imported TLS certificates; ACME is handled by Goma. |
|
services/cluster
Package cluster drives Docker Swarm as Miabi's optional cluster mode, one swarm per cluster.
|
Package cluster drives Docker Swarm as Miabi's optional cluster mode, one swarm per cluster. |
|
services/config
Package config owns workspace configuration files: named text payloads, encrypted at rest, projected into containers as read-only files.
|
Package config owns workspace configuration files: named text payloads, encrypted at rest, projected into containers as read-only files. |
|
services/controlmanager
Package controlmanager watches for workloads that disappeared from under Miabi: an app whose active release container is gone from its node, a service app whose swarm service is gone from its cluster, and a volume whose data is gone from its node.
|
Package controlmanager watches for workloads that disappeared from under Miabi: an app whose active release container is gone from its node, a service app whose swarm service is gone from its cluster, and a volume whose data is gone from its node. |
|
services/crypto
Package crypto provides AES-GCM encryption for secrets stored at rest.
|
Package crypto provides AES-GCM encryption for secrets stored at rest. |
|
services/customrole
Package customrole manages admin-defined roles (permission sets) and enforces the cardinal RBAC rule: no privilege escalation.
|
Package customrole manages admin-defined roles (permission sets) and enforces the cardinal RBAC rule: no privilege escalation. |
|
services/database
Package database provisions database server instances (PostgreSQL, MySQL, MariaDB, Redis) as containers and manages the logical databases they host, so a single instance can back many apps instead of one container per database.
|
Package database provisions database server instances (PostgreSQL, MySQL, MariaDB, Redis) as containers and manages the logical databases they host, so a single instance can back many apps instead of one container per database. |
|
services/dbupgrade
Package dbupgrade adapts the application and backup services to the small interfaces the database version-upgrade orchestration depends on, so both the API server and the worker can wire them without the database package importing application or backup, which would cycle.
|
Package dbupgrade adapts the application and backup services to the small interfaces the database version-upgrade orchestration depends on, so both the API server and the worker can wire them without the database package importing application or backup, which would cycle. |
|
services/directory
Package directory turns a successful LDAP/Active-Directory bind into a Miabi user: it just-in-time provisions the account and reconciles directory groups onto platform-admin and per-workspace access.
|
Package directory turns a successful LDAP/Active-Directory bind into a Miabi user: it just-in-time provisions the account and reconciles directory groups onto platform-admin and per-workspace access. |
|
services/dnsprovider
Package dnsprovider manages workspace DNS provider connections: connect, test, list, delete.
|
Package dnsprovider manages workspace DNS provider connections: connect, test, list, delete. |
|
services/dockerimport
Package dockerimport adopts pre-existing Docker resources into Miabi without tearing down what is running.
|
Package dockerimport adopts pre-existing Docker resources into Miabi without tearing down what is running. |
|
services/domain
Package domain manages workspace-owned domains: registration, DNS-verified ownership, and the default TLS policy routes inherit.
|
Package domain manages workspace-owned domains: registration, DNS-verified ownership, and the default TLS policy routes inherit. |
|
services/edgegateway
Package edgegateway provisions the Goma Gateway container fronting an edge-gateway node's public ingress.
|
Package edgegateway provisions the Goma Gateway container fronting an edge-gateway node's public ingress. |
|
services/environment
Package environment manages promotion stages (dev → staging → prod) within a workspace.
|
Package environment manages promotion stages (dev → staging → prod) within a workspace. |
|
services/eventbus
Package eventbus is a lightweight in-process publish/subscribe bus used to fan out live events (e.g.
|
Package eventbus is a lightweight in-process publish/subscribe bus used to fan out live events (e.g. |
|
services/events
Package events records and serves resource timeline events: lifecycle transitions, runtime container events, and configuration changes.
|
Package events records and serves resource timeline events: lifecycle transitions, runtime container events, and configuration changes. |
|
services/gitops
Package gitops is the declarative, pull-based half of Miabi's GitOps and CI/CD model.
|
Package gitops is the declarative, pull-based half of Miabi's GitOps and CI/CD model. |
|
services/gitrepo
Package gitrepo manages stored Git credentials used to clone private repositories at build time.
|
Package gitrepo manages stored Git credentials used to clone private repositories at build time. |
|
services/gpu
Package gpu inventories the physical GPUs on Miabi-managed nodes and resolves a running app's GPU request to concrete devices at deploy time.
|
Package gpu inventories the physical GPUs on Miabi-managed nodes and resolves a running app's GPU request to concrete devices at deploy time. |
|
services/housekeeping
Package housekeeping reconciles a node's real Docker state against what Miabi intends, serving three faces of drift: a disk report, a safe categorized prune with a dry-run preview, and a reconcile that classifies orphan/missing/untracked by joining live Docker against the DB by the miabi.* labels.
|
Package housekeeping reconciles a node's real Docker state against what Miabi intends, serving three faces of drift: a disk report, a safe categorized prune with a dry-run preview, and a reconcile that classifies orphan/missing/untracked by joining live Docker against the DB by the miabi.* labels. |
|
services/image
Package image manages the built-image catalog: provenance written by the pipeline build step, read APIs for the UI, and a retention GC that never collects a digest a live deployment or pinned release references.
|
Package image manages the built-image catalog: provenance written by the pipeline build step, read APIs for the UI, and a retention GC that never collects a digest a live deployment or pinned release references. |
|
services/job
Package job runs one-off commands in an application's runtime context (a Job) and the schedules that spawn them (a CronJob).
|
Package job runs one-off commands in an application's runtime context (a Job) and the schedules that spawn them (a CronJob). |
|
services/keyring
Package keyring manages per-workspace data-encryption keys.
|
Package keyring manages per-workspace data-encryption keys. |
|
services/logintoken
Package logintoken issues the short-lived personal API token behind the console's "Copy login command" flow.
|
Package logintoken issues the short-lived personal API token behind the console's "Copy login command" flow. |
|
services/mailer
Package mailer sends Miabi's own platform notification emails — password resets, workspace invitations, account welcomes — over a system SMTP server.
|
Package mailer sends Miabi's own platform notification emails — password resets, workspace invitations, account welcomes — over a system SMTP server. |
|
services/managedcert
Package managedcert issues and renews TLS certificates via ACME DNS-01 using a workspace's connected DNS provider, storing the result in the workspace Certificates.
|
Package managedcert issues and renews TLS certificates via ACME DNS-01 using a workspace's connected DNS provider, storing the result in the workspace Certificates. |
|
services/marketplace
Package marketplace provides the declarative template catalog (loaded from the embedded official source) and installs templates by orchestrating the application, database, storage and stack services.
|
Package marketplace provides the declarative template catalog (loaded from the embedded official source) and installs templates by orchestrating the application, database, storage and stack services. |
|
services/marketplace/manifest
Package manifest defines the declarative Miabi template format (apiVersion miabi.io/v1, kind Template): a versioned bundle describing a whole stack of applications plus the databases and volumes they depend on.
|
Package manifest defines the declarative Miabi template format (apiVersion miabi.io/v1, kind Template): a versioned bundle describing a whole stack of applications plus the databases and volumes they depend on. |
|
services/marketplace/remote
Package remote syncs the Miabi marketplace registry from the standalone marketplace service into a local cache, so the in-Miabi catalog can serve it alongside the embedded floor without a per-request round trip.
|
Package remote syncs the Miabi marketplace registry from the standalone marketplace service into a local cache, so the in-Miabi catalog can serve it alongside the embedded floor without a per-request round trip. |
|
services/middleware
Package middleware manages Goma Gateway middlewares owned by workspaces and reconciles them into the proxy provider.
|
Package middleware manages Goma Gateway middlewares owned by workspaces and reconciles them into the proxy provider. |
|
services/monitoring
Package monitoring exposes container metrics and workspace health overviews.
|
Package monitoring exposes container metrics and workspace health overviews. |
|
services/netalloc
Package netalloc hands out non-overlapping subnets, carved from a single platform pool, for every Docker network Miabi creates.
|
Package netalloc hands out non-overlapping subnets, carved from a single platform pool, for every Docker network Miabi creates. |
|
services/network
Package network manages Docker networks owned by workspaces.
|
Package network manages Docker networks owned by workspaces. |
|
services/node
Package node manages Docker host (server) records and their reachability.
|
Package node manages Docker host (server) records and their reachability. |
|
services/notify
Package notify turns persisted application events into outbound notifications: it fans an event out to a workspace's webhooks and channels, and renders/sends channel messages.
|
Package notify turns persisted application events into outbound notifications: it fans an event out to a workspace's webhooks and channels, and renders/sends channel messages. |
|
services/oauth
Package oauth implements the OAuth 2.0 / OpenID Connect authorization-code login flow against admin-configured providers.
|
Package oauth implements the OAuth 2.0 / OpenID Connect authorization-code login flow against admin-configured providers. |
|
services/pipeline
Package pipeline implements Miabi's CI/CD: pipeline-as-code versioned with the app, PipelineRun lifecycle, and the internal runner that executes steps in isolated containers.
|
Package pipeline implements Miabi's CI/CD: pipeline-as-code versioned with the app, PipelineRun lifecycle, and the internal runner that executes steps in isolated containers. |
|
services/placement
Package placement decides where a new resource lands: a location (cluster) the workspace may use, then a node inside it.
|
Package placement decides where a new resource lands: a location (cluster) the workspace may use, then a node inside it. |
|
services/platformbackup
Package platformbackup is the admin-only disaster-recovery feature for Miabi's own control plane.
|
Package platformbackup is the admin-only disaster-recovery feature for Miabi's own control plane. |
|
services/platformimage
Package platformimage is the deployment-config image catalog: the single source of truth for every container image the platform itself runs.
|
Package platformimage is the deployment-config image catalog: the single source of truth for every container image the platform itself runs. |
|
services/platformrestore
Package platformrestore rebuilds a Miabi platform onto a fresh host from a recovery point.
|
Package platformrestore rebuilds a Miabi platform onto a fresh host from a recovery point. |
|
services/portbinding
Package portbinding manages host port binding requests.
|
Package portbinding manages host port binding requests. |
|
services/portforward
Package portforward gives on-demand external access to a managed database without publishing a host port.
|
Package portforward gives on-demand external access to a managed database without publishing a host port. |
|
services/quota
Package quota enforces per-workspace plan limits and capabilities.
|
Package quota enforces per-workspace plan limits and capabilities. |
|
services/recovery
Package recovery finishes what `miabi restore` starts.
|
Package recovery finishes what `miabi restore` starts. |
|
services/registration
Package registration owns self-service sign-up: whether it is open, who may take it, and what state a new account lands in.
|
Package registration owns self-service sign-up: whether it is open, who may take it, and what state a new account lands in. |
|
services/registry
Package registry manages stored container-registry credentials used to pull private images at deploy time.
|
Package registry manages stored container-registry credentials used to pull private images at deploy time. |
|
services/registryserver
Package registryserver runs and authorizes the platform's built-in, multi-tenant Docker registry.
|
Package registryserver runs and authorizes the platform's built-in, multi-tenant Docker registry. |
|
services/release
Package release turns the per-application Release — a deployed, rollback-able version — into a promotable artifact: a workspace-wide catalog with provenance, approval gates per environment, and promotion (re-pointing an application at a release) that the gate guards.
|
Package release turns the per-application Release — a deployed, rollback-able version — into a promotable artifact: a workspace-wide catalog with provenance, approval gates per environment, and promotion (re-pointing an application at a release) that the gate guards. |
|
services/route
Package route manages Goma Gateway routes bound to applications and reconciles them into the proxy provider.
|
Package route manages Goma Gateway routes bound to applications and reconciles them into the proxy provider. |
|
services/runner
Package runner manages build/pipeline runner records: registration, scope (workspace-owned vs platform-shared), labels, concurrency and reachability.
|
Package runner manages build/pipeline runner records: registration, scope (workspace-owned vs platform-shared), labels, concurrency and reachability. |
|
services/secret
Package secret is the Vault: workspace-scoped named secrets that env var values reference (`${{ secrets.NAME }}`) and that are resolved into a container's environment at deploy or job time.
|
Package secret is the Vault: workspace-scoped named secrets that env var values reference (`${{ secrets.NAME }}`) and that are resolved into a container's environment at deploy or job time. |
|
services/session
Package session maintains a Redis-backed revocation list for JWT sessions, keyed by the token's jti claim.
|
Package session maintains a Redis-backed revocation list for JWT sessions, keyed by the token's jti claim. |
|
services/settings
Package settings provides cached, typed access to platform-wide key/value settings stored in the database.
|
Package settings provides cached, typed access to platform-wide key/value settings stored in the database. |
|
services/stack
Package stack groups related applications in a workspace.
|
Package stack groups related applications in a workspace. |
|
services/storage
Package storage manages persistent (Docker) volumes owned by workspaces.
|
Package storage manages persistent (Docker) volumes owned by workspaces. |
|
services/twofactor
Package twofactor wraps TOTP (RFC 6238) generation and validation for time-based two-factor authentication.
|
Package twofactor wraps TOTP (RFC 6238) generation and validation for time-based two-factor authentication. |
|
services/updatecheck
Package updatecheck asks GitHub, once a day, whether a newer Miabi release exists and caches the answer for the dashboard.
|
Package updatecheck asks GitHub, once a day, whether a newer Miabi release exists and caches the answer for the dashboard. |
|
services/usersettings
Package usersettings owns per-user preferences: the console's look and locale, and which workspace a client lands on when it has none in mind.
|
Package usersettings owns per-user preferences: the console's look and locale, and which workspace a client lands on when it has none in mind. |
|
services/volumebackup
Package volumebackup archives a managed volume's contents to the workspace's S3 target using the ecosystem volume-bkup tool as a one-shot container, and restores it.
|
Package volumebackup archives a managed volume's contents to the workspace's S3 target using the ecosystem volume-bkup tool as a one-shot container, and restores it. |
|
services/webhook
Package webhook manages workspace webhooks and the signing/delivery of their JSON payloads.
|
Package webhook manages workspace webhooks and the signing/delivery of their JSON payloads. |
|
services/workspace
Package workspace manages workspaces, memberships, and invitations.
|
Package workspace manages workspaces, memberships, and invitations. |
|
services/wsbackup
Package wsbackup exports a workspace to a portable bundle on S3 and restores one back.
|
Package wsbackup exports a workspace to a portable bundle on S3 and restores one back. |
|
siem
Package siem streams the audit log to external SIEM sinks at-least-once, gated on the siem_stream entitlement and entirely off the request path.
|
Package siem streams the audit log to external SIEM sinks at-least-once, gated on the siem_stream entitlement and entirely off the request path. |
|
slug
Package slug derives URL/DNS-safe identifiers from human names.
|
Package slug derives URL/DNS-safe identifiers from human names. |
|
storage/blob
Package blob is a minimal S3/MinIO object client for the few places Miabi must touch an object store directly from Go: a bundle's control objects and bucket listings, and `miabi restore`, which reads a sealed envelope on a bare host before any platform exists.
|
Package blob is a minimal S3/MinIO object client for the few places Miabi must touch an object store directly from Go: a bundle's control objects and bucket listings, and `miabi restore`, which reads a sealed envelope on a bare host before any platform exists. |
|
storage/logbackfill
Package logbackfill migrates pre-existing large log rows out of Postgres into the shared log store.
|
Package logbackfill migrates pre-existing large log rows out of Postgres into the shared log store. |
|
storage/migration/upgrade
Package upgrade runs ordered, versioned data-upgrade steps.
|
Package upgrade runs ordered, versioned data-upgrade steps. |
|
web
Package web embeds the built frontend (the Vue SPA) into the Go binary so a single `miabi` executable serves both the API and the UI.
|
Package web embeds the built frontend (the Vue SPA) into the Go binary so a single `miabi` executable serves both the API and the UI. |
|
worker
Package worker holds the asynq producer, task types, and handlers for background work (deploys, backups, metric scrapes, ...).
|
Package worker holds the asynq producer, task types, and handlers for background work (deploys, backups, metric scrapes, ...). |
|
wsbundle
Package wsbundle holds the format of a Miabi Portable Bundle: one workspace, its configuration, secrets and data, written to an S3 bucket as a self-describing set of objects.
|
Package wsbundle holds the format of a Miabi Portable Bundle: one workspace, its configuration, secrets and data, written to an S3 bucket as a self-describing set of objects. |
|
pkg
|
|
|
stack
Package platformstack installs and updates Miabi's own stack directly against the Docker API, with every component tagged io.miabi.managed-by=miabi.
|
Package platformstack installs and updates Miabi's own stack directly against the Docker API, with every component tagged io.miabi.managed-by=miabi. |
|
stack/docker
Package docker is the Docker seam the platform-stack engine talks through.
|
Package docker is the Docker seam the platform-stack engine talks through. |
|
stack/saferollout
Package saferollout replaces a running container with a new image without a blind cutover.
|
Package saferollout replaces a running container with a new image without a blind cutover. |
|
stack/selfcontainer
Package selfcontainer detects the Docker container ID of the running process, so Miabi can recognise its own container and refuse to stop or delete it from the admin containers list — which would take the platform offline.
|
Package selfcontainer detects the Docker container ID of the running process, so Miabi can recognise its own container and refuse to stop or delete it from the admin containers list — which would take the platform offline. |
|
stack/stackcmd
Package stackcmd is the behaviour behind the host-side verbs — install/converge, upgrade, restart, status and uninstall — with no command-line framework attached.
|
Package stackcmd is the behaviour behind the host-side verbs — install/converge, upgrade, restart, status and uninstall — with no command-line framework attached. |
|
Package templates embeds a minimal offline floor of the official Miabi marketplace catalog — the core data and infra primitives — so the binary works out of the box without network access.
|
Package templates embeds a minimal offline floor of the official Miabi marketplace catalog — the core data and infra primitives — so the binary works out of the box without network access. |
|
gen
command
Command gen vendors the official templates from the marketplace registry's published export.json into miabi/templates/, the embedded offline floor.
|
Command gen vendors the official templates from the marketplace registry's published export.json into miabi/templates/, the embedded offline floor. |